About the Exam

CRISC is ISACA’s certification for professionals who identify and manage enterprise IT risk and implement and maintain information systems controls. The exam covers four domains: governance, risk assessment, risk response and reporting, and technology and security. Passing the exam demonstrates knowledge of real-world risk and control practices used in enterprise IT environments.

Exam Topics

  • Governance26%
  • Risk Assessment22%
  • Risk Response and Reporting32%
  • Technology and Security20%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated July 14, 2026 at 5:21 PM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Risk Assessment

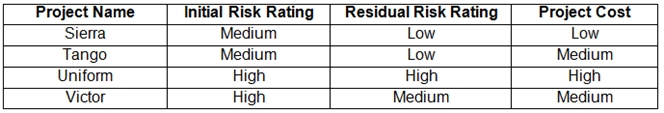
What can be determined from the risk-scenario chart?
Question Image

Explanation

Initial and residual risk ratings allow the relative placement of projects by risk level to be compared on a risk map, including how their positions change after risk treatment.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Risk Response and Reporting

Which of the following is the BEST control for mitigating risk when a critical customer-facing application has been vulnerable to recent credential-stuffing attacks?

Explanation

Multi-factor authentication requires an additional verification factor beyond a username and password, preventing successful account access with stolen credential pairs alone. It directly mitigates credential-stuffing attacks.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

Risk Assessment

Which of the following offers the MOST useful input for developing IT risk scenarios?

Explanation

Risk factors influence the frequency and/or business impact of IT risk scenarios. Considering both internal factors that the enterprise can influence and external factors outside its control provides the broadest and most relevant basis for developing scenarios.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Risk Assessment

Which of the following is the PRIMARY input for designing IT controls?

Explanation

IT controls should be designed using identified internal and external risks as the primary input, so that control objectives and activities directly mitigate relevant threats, vulnerabilities, and potential business impacts. Industry standards, self-assessments, and expert recommendations are useful supporting inputs but do not replace risk-based control selection.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Governance

Which of the following provides the BEST evidence of an effective internal control environment?

Explanation

Independent audit results are the strongest evidence because they provide an objective assessment of whether internal controls are appropriately designed and operating effectively.

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home