About the Exam

The CCIS exam is intended for identity and access management professionals, analysts focused on identity-based threats, and policy and access administrators. It tests knowledge and skills for managing Falcon Identity Protection, including identity-based risk, policy rules, MFA and IDaaS connectors, threat hunting, and incident investigation. Passing demonstrates the candidate can respond to identity-based detections and manage an organization's identity security posture within the CrowdStrike Falcon platform.

Exam Topics

  • Zero Trust Architecture8%
  • Identity Protection Tenets8%
  • Falcon Identity Protection Fundamentals8%
  • Domain Security Assessment8%
  • Risk Assessment8%
  • User Assessment8%
  • Threat Hunting and Investigation8%
  • Risk Management with Policy Rules8%
  • Configuration and Connectors8%
  • MFA and IDAAS Configuration Basics8%
  • Falcon Fusion for Identity Protection8%
  • GraphQL API8%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated April 9, 2026 at 9:41 PM
Topic filter
Question status
Question sort
Questions per page

QuestionQ1

VerifiedRisk Assessment

To lower a domain risk score, you need to:

Explanation

Domain risk is lowered by remediating each identified risk on its related entities. Falcon Identity Protection provides Recommended Actions to mitigate the risk; completing those actions removes or reduces the underlying conditions contributing to the domain risk score.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

VerifiedRisk Management with Policy Rules

What action is recommended for the “Guest Account Enabled” risk?

Explanation

Guest accounts should be disabled on endpoints unless their use is explicitly necessary, because they can allow anonymous access. The corrective action is to disable Guest accounts on all endpoints where they are enabled.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

VerifiedRisk Management with Policy Rules

Which section of the Falcon Identity Protection module is used to manage your Policy Rule groups?

Explanation

Falcon Identity Protection policy rules are managed in the Enforce section. CrowdStrike documents Policy Rules as an Enforce resource used to create, edit, and manage rules, so Policy Rule groups are managed under Enforce.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

VerifiedFalcon Fusion for Identity Protection

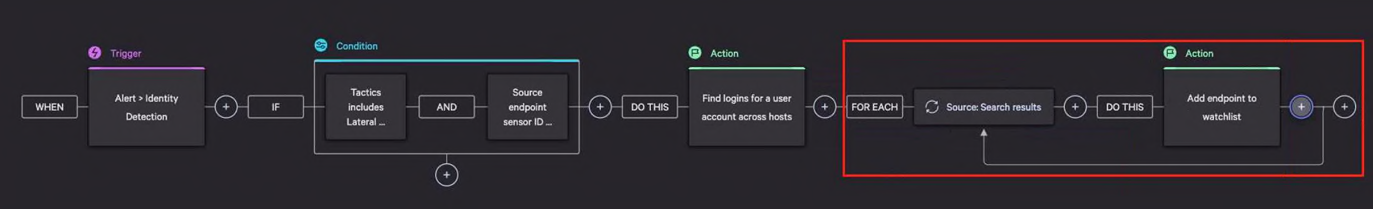
Which role is able to create a Falcon Fusion workflow for Identity Detections?

Explanation

The Workflow Author role grants the capability to build Falcon Fusion workflows, including workflows that use Identity Detections as their trigger.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

VerifiedFalcon Identity Protection Fundamentals

Which option BEST explains how Falcon Identity Protection can enhance an organization’s security?

Explanation

Falcon Identity Protection provides identity threat detection and response across Active Directory and cloud identity providers. It helps identify Active Directory misconfigurations and vulnerabilities, detects identity-based threats, and supports prevention and response to attacks such as compromised-credential abuse and lateral movement.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home