About the Exam

CrowdStrike certification for investigative analysts who perform deeper detection analysis, response and proactive threat hunting on the Falcon platform. It covers event search and query syntax, machine timelining, hunting methodology, insider-threat and proactive investigations, and the interpretation of detection telemetry. Passing demonstrates practical threat-hunting skill rather than platform administration.

Exam Topics

  • ATT&CK Frameworks0%
  • Detection Analysis0%
  • Search and Investigation Tools0%
  • Event Search0%
  • Reports and References0%
  • Hunting Analytics0%
  • Hunting Methodology0%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated March 17, 2026 at 10:58 PM

Topic filter
Question status
Question sort
Questions per page

QuestionQ1

VerifiedEvent Search

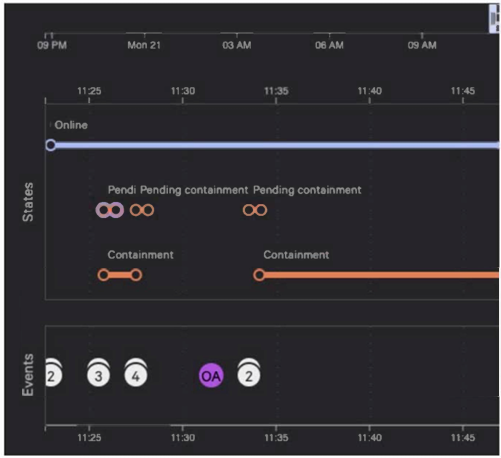
Refer to the image.

Question Image

Why are there six pending-containment events?

Explanation

A device-containment operation produces an event when the containment change is requested and a corresponding event when the request reaches its completed status. Thus, three containment operations create six pending-containment events.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

VerifiedEvent Search

You are investigating several NetworkConnectIP4 events, all with the same ContextProcessId of 123456789.

Which query will display the process responsible for these NetworkConnectIP4 events?

Explanation

For CrowdStrike network events, ContextProcessId correlates to TargetProcessId in ProcessRollup2 and SyntheticProcessRollup2 process events. Filtering those process events for TargetProcessId = 123456789 identifies the process responsible for the network connections.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

VerifiedEvent Search

Falcon is producing detections for a malicious file, evil.exe, across several hosts and varying file paths as end users try to run it.

Which query can proactively hunt for locations where the file exists before a user executes it?

Explanation

A broad hunt should search both ProcessRollup2 and SyntheticProcessRollup2 telemetry, match evil.exe case-insensitively, extract the final filename from the image path, and aggregate the results by host, path, and command-line details. This identifies occurrences across hosts without limiting the search to a single agent ID or a particular user-path pattern.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

VerifiedEvent Search

You have created an Advanced Event Search query to identify suspicious PowerShell usage and want to show its results on a dashboard.

How can you display this query in a dashboard?

Explanation

CrowdStrike Falcon custom dashboards can display Advanced Event Search output by creating a customized dashboard widget from the search query. A saved search, scheduled search, or scheduled workflow serves a different purpose and does not directly add the query results to a dashboard.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

VerifiedEvent Search

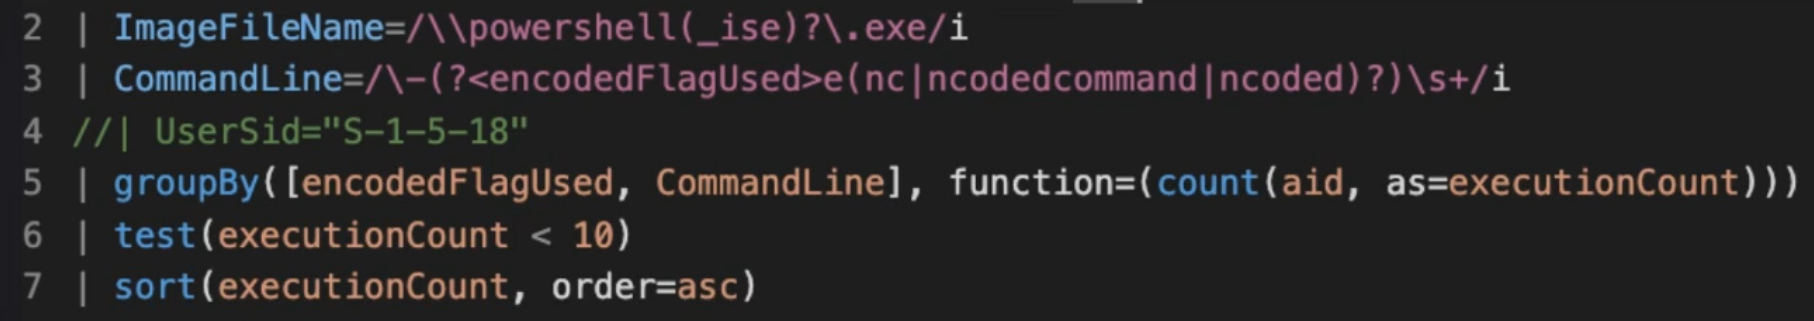
Which statement filters all events associated with a new scheduled task registered by the user "Doris"?
Explanation

The NewScheduledTaskRegistered event identifies the registration of a new scheduled task, and UserName="Doris" restricts the results to tasks registered by Doris.

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home