An analyst receives an alert that a user clicked on a malicious link. The analyst verifies that the link is malicious and was intended to capture credentials. The analyst verifies that the user visited the website, but no evidence indicates that the credentials were used. The analyst recommends that the user take remedial training and closes the case.
Which of the following steps in the incident response process did the analyst neglect?
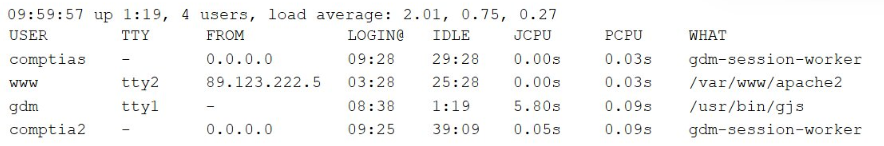
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network. Which of the following artifacts should the analyst collect first?
Community Discussion
Which of the following activities takes place during the analysis phase of the incident response process?
Community Discussion
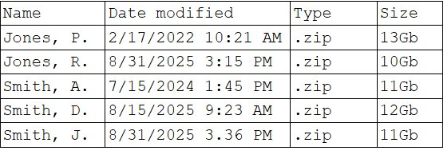
An incident response team is investigating a possible data leak, and various IT systems are used to collect evidence. Which of the following processes is required to ensure that evidentiary artifacts are properly recorded?
Community Discussion
Which of the following phases of the incident response process will permanently remove an attacker's access to corporate resources?

Community Discussion