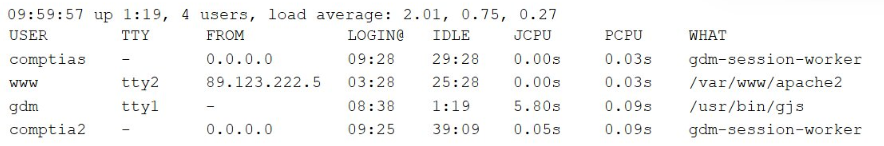
The session list shows the 'www' account—the service account that runs the Apache web server—logged in interactively from an external IP address (89.123.222.5) via tty2, executing /var/www/apache2. Service accounts used to run web server processes are not intended to have interactive login sessions, especially not from remote/public IP addresses. This pattern indicates that an attacker exploited the web application to gain a shell as the web service user, effectively initiating an unauthorized session on the server. The other options do not fit: resource usage (JCPU/PCPU) is minimal, the number of concurrent users (4) is not unusual, and the idle times shown are within normal ranges for active sessions.
Community Discussion