About the Exam

CompTIA SecurityX is an advanced, performance-based cybersecurity certification for experienced security architects and senior security engineers. The exam measures the ability to architect, engineer, integrate, and implement secure solutions across complex enterprise environments, including cloud, on-premises, and hybrid settings. It also covers governance, risk and compliance, automation, monitoring, detection, incident response, and cryptographic technologies. Passing demonstrates expert-level readiness to assess and improve enterprise cybersecurity.

Exam Topics

  • Governance, Risk, and Compliance20%
  • Security Architecture27%
  • Security Engineering31%
  • Security Operations22%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated August 26, 2026 at 2:49 AM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Security Operations

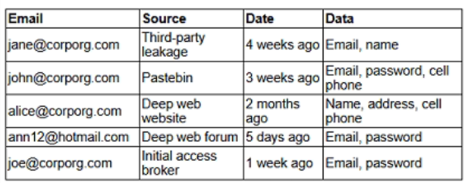
A security engineer receives an alert from the threat-intelligence platform containing the following information:
Question Image

Which action should the security engineer take first?

Explanation

Accounts for John, Ann, and Joe have exposed passwords and should have their credentials reset immediately. Disconnecting their active sessions also invalidates existing authenticated access that could be held by an unauthorized party, providing immediate containment.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Security Engineering

A recent SAST scan of an application that supplies an encrypted tunnel between sites detected the following vulnerability:

Cipher Block Chaining Initialization Vector must be unpredictable.

The vulnerability was identified on these source-code lines:

iv = b"CompTIAIV202512"  
cipher= Cipher(Algorithms.AES(key), modes.CBC(iv))  

Which of the following is a potential impact of this vulnerability?

Explanation

CBC requires an unpredictable IV for each encryption operation because the IV is combined with the first plaintext block. A fixed, predictable IV removes this protection and can enable confidentiality attacks that reveal or allow inference of protected plaintext. NIST SP 800-38A specifies that CBC IVs need not be secret but must be unpredictable.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

Security Operations

A security administrator has isolated a computer system because it was targeted by a ransomware attack. Which of the following should the security administrator do to recover from this attack in the most secure way?

Explanation

Restoring the isolated system from a known-good baseline snapshot avoids the uncertainty of relying on the attacker's cooperation or on artifacts that may themselves be compromised, making it the most secure recovery path. File versioning may have been created or tampered with during the attack window and cannot be trusted as a clean source, attempting to recover the encryption key is unreliable and does not guarantee removal of any implanted malware, and paying the ransom funds criminal activity while providing no assurance that a working decryption key will be delivered, so security guidance from bodies such as CISA and NIST explicitly discourages it in favor of restoring from verified clean backups or baselines.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Governance, Risk, and Compliance

A security architect is analyzing an old application that is not covered for maintenance anymore because the software company is no longer in business. Which of the following techniques should have been implemented to prevent these types of risks?

Explanation

A source code escrow places the application's source code with a neutral third party that releases it to the customer if the vendor goes out of business, stops support, or otherwise fails to meet contractual maintenance obligations, which is exactly the scenario described. Code reviews, supply chain visibility, and software audits improve quality and risk awareness at the time they are performed but do nothing to guarantee continued access to or maintainability of the code once the vendor disappears.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Security Operations

Which of the following is the best reason for obtaining file hashes from a confiscated laptop?
Explanation

File hashes serve as forensic integrity proofs. By computing and recording hashes at the time of seizure, investigators can later verify that files remain unchanged through comparison of hash values. This preserves evidentiary value and maintains chain of custody integrity for court proceedings. Hashes detect tampering (they don't prevent it), and while they create unique identifiers, the primary forensic purpose is validation of file integrity over time.

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home