About the Exam

CompTIA SecurityX is CompTIA's expert-level cybersecurity certification for experienced security professionals focused on enterprise security architecture, engineering, and governance. CA1-005 was the beta exam version listed by CompTIA while SecurityX was under development. Passing demonstrates the ability to assess enterprise security readiness and design secure solutions across cloud, on-premises, and hybrid environments.

Exam Topics

  • Governance, Risk, and Compliance25%
  • Security Architecture20%
  • Security Engineering23%
  • Security Operations25%
  • Security Program Management and Oversight7%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated December 1, 2025 at 10:54 AM

Topic filter
Question status
Question sort
Questions per page

QuestionQ1

VerifiedGovernance, Risk, and Compliance

A security analyst identifies a possible RAT infection on a computer in the internal network. After reviewing the alert details, the analyst determines that the attack’s initial vector was an email forwarded to multiple recipients within the same organizational unit. Which of the following should the analyst do first to minimize this type of threat in the future?

Explanation

A security awareness program teaches users to recognize, avoid, and report phishing and other suspicious emails, reducing the likelihood that a malicious message will be opened, acted on, or forwarded to additional recipients. CISA recommends user training and awareness as a critical component of counter-phishing defenses.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

VerifiedSecurity Operations

A web application server that supports hybrid modern and legacy financial applications recently received a scheduled upgrade of common libraries, including OpenSSL. Multiple users now report unsuccessful attempts to connect to the server. The technician conducting initial triage identified the following:

  • Client applications older than five years appear to be affected most.
  • Web-server logs show initial connection attempts from affected hosts.
  • For the unsuccessful connections, the logs report "cipher unavailable."

Which of the following is the most likely safe remediation for this situation?

Explanation

Older clients must be updated to negotiate a secure cipher suite supported by the upgraded server, such as AES-GCM with TLS 1.2 or later. OpenSSL documents AES-GCM cipher suites as TLS 1.2 suites and prohibits SSL 3.0 at security level 2. ECB is not a safe TLS mode, and a server signature-algorithm change does not resolve a cipher-suite mismatch.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

VerifiedSecurity Operations

A user attempted to open the web page at http://10.1.1.1. The page previously did not require authentication, but the browser now prompts for credentials. Which action would best prevent the issue from happening again and lower the likelihood of credential exposure?

Explanation

Plain HTTP does not protect authentication data in transit. Configuring the web server to use X.509 certificates enables TLS-protected authentication, reducing the risk that credentials are exposed through interception or service impersonation.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

VerifiedSecurity Operations

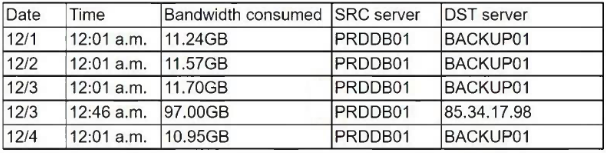
A security operations analyst is reviewing network-traffic baselines for nightly database backups. Given the following information:
Question Image

Which action should the security analyst take next?

Explanation

A 97 GB transfer from PRDDB01 to an external IP address, at a time different from the normal backup window, deviates sharply from the usual approximately 11 GB transfers to BACKUP01. This is a potential security incident, so the established incident response playbook should guide validation, escalation, containment, and evidence-handling actions.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

VerifiedSecurity Engineering

A company requires a highly secure way to transfer documents across an insecure network. The documents are highly sensitive, and their encryption must remain guaranteed even if network traffic is intercepted. Which encryption technique is the best option?

Explanation

A one-time pad can provide perfect secrecy: with a truly random secret key that is at least as long as the plaintext and used only once, intercepted ciphertext reveals no information about the document.

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home