About the Exam

This 90-minute Cisco exam covers implementing secure remote communications with VPN solutions on Cisco routers and firewalls, including secure communications, architectures, and troubleshooting. It is associated with the CCNP Security certification and passing it earns the Cisco Certified Specialist - Network Security VPN Implementation certification. It is intended for CCNP Security candidates and network security engineers working with site-to-site and remote access VPNs.

Exam Topics

  • Site-to-site Virtual Private Networks on Routers and Firewalls15%
  • Remote access VPNs20%
  • Troubleshooting using ASDM and CLI35%
  • Secure Communications Architectures30%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated July 9, 2026 at 9:15 PM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Site-to-site Virtual Private Networks on Routers and Firewalls

An engineer is troubleshooting a new DMVPN configuration on a Cisco IOS router. After issuing the show crypto isakmp sa command, the returned response is MM_NO_STATE. Why does this failure occur?

Explanation

An ISAKMP MM_NO_STATE result means that an IKE/ISAKMP Phase 1 security association has not been established. The peers must have matching Phase 1 policy parameters, such as authentication method, encryption, hash, Diffie-Hellman group, and lifetime, for the negotiation to proceed.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Remote access VPNs

Which two web-resource types or protocols are enabled by default on the Cisco ASA Clientless SSL VPN portal?

Choose two
Explanation

The Clientless SSL VPN portal provides built-in access to HTTP/HTTPS web resources and CIFS file shares. ICA, VNC, and RDP depend on separately configured client-server plug-ins rather than being enabled by default.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

Remote access VPNs

A Cisco AnyConnect client creates an SSL VPN connection to an ASA at the corporate office. An engineer must make sure that the client computer complies with the enterprise security policy. Which feature can update the client so it meets an enterprise security policy?

Explanation

Advanced Endpoint Assessment enhances Host Scan with remediation actions that can attempt to update noncompliant computers to meet required version requirements, enabling the endpoint to satisfy the enterprise security policy.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Troubleshooting using ASDM and CLI
Question Image

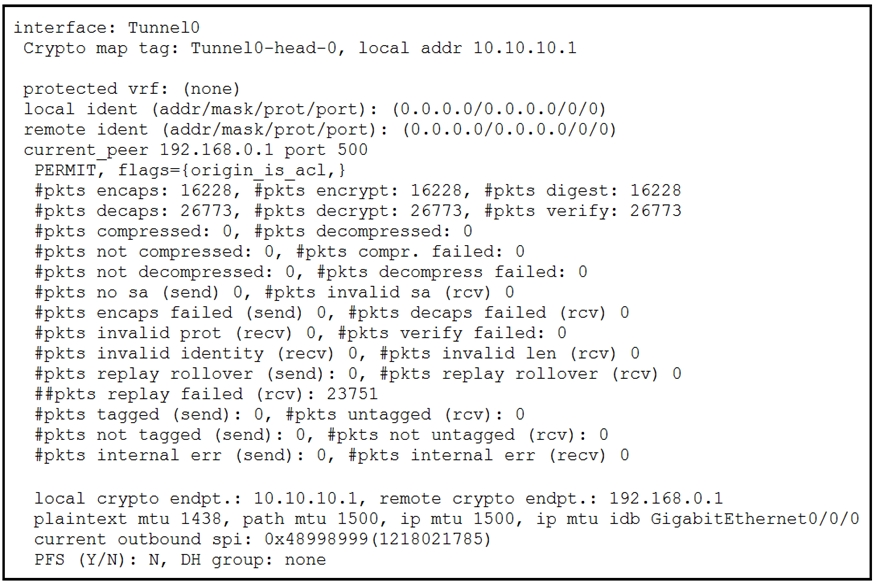
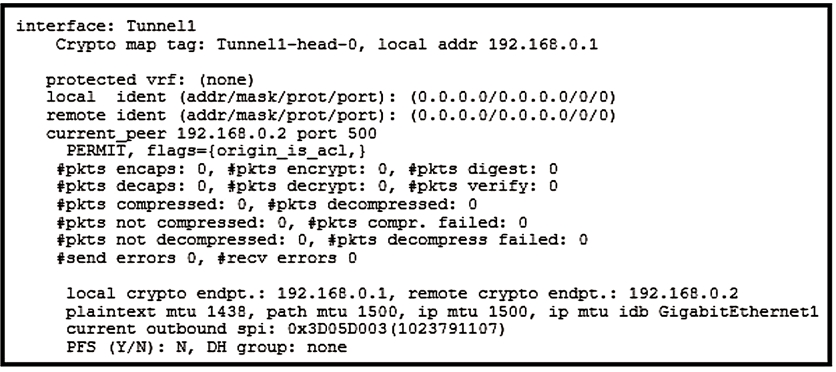
Refer to the exhibit. Which two tunnel types generate the displayed show crypto ipsec sa output?

Choose two
Explanation

Route-based IPsec virtual tunnel interfaces create an automatically generated Tunnel<number>-head-0 crypto-map entry and commonly use any-to-any IPsec traffic selectors. FlexVPN is built on this tunnel-interface/VTI model, so both FlexVPN and VTI can produce this form of IPsec SA output. GRE and DMVPN tunnel protection instead identifies GRE traffic with IP protocol 47, whereas a conventional crypto map is typically associated with a physical interface and ACL-selected traffic.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Site-to-site Virtual Private Networks on Routers and Firewalls
Question Image

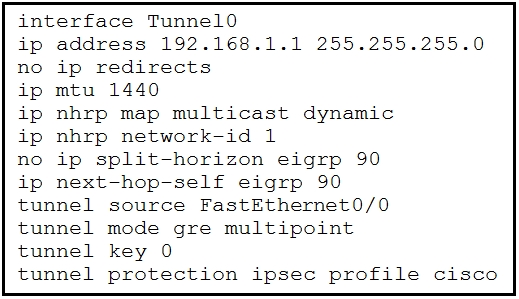
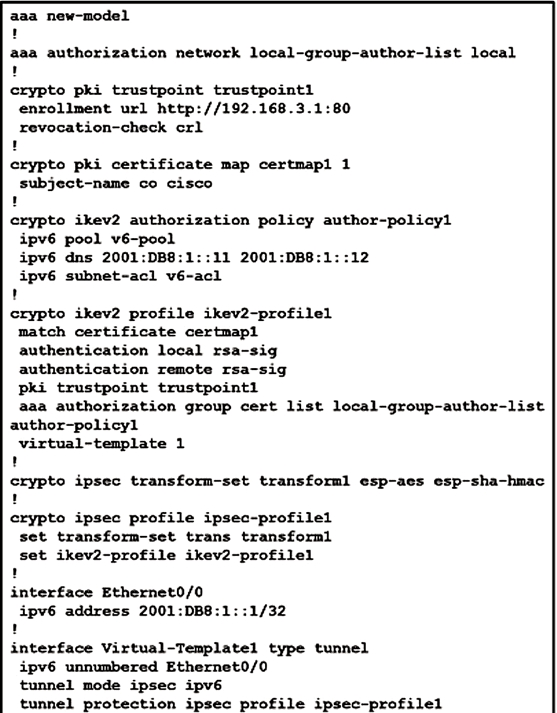
Refer to the exhibit. What does this command set configure?

Explanation

A FlexVPN server supports an IPv6 dVTI session when its IKEv2 profile is associated with a virtual template and the virtual template is configured for tunnel mode ipsec ipv6. The IPv6 address pool, DNS servers, and subnet ACL are supplied through the IKEv2 authorization policy; authentication is certificate-based RSA signatures with local AAA group authorization.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home