About the Exam

This 90-minute exam is for CCNP Security candidates who work with Cisco Identity Services Engine (ISE). It covers ISE architecture and deployment, policy enforcement, Web Auth and guest services, profiler, Bring Your Own Device (BYOD), endpoint compliance, and network access device administration. Passing earns the Cisco Certified Specialist - Security Identity Management Implementation certification and can satisfy the concentration exam requirement for CCNP Security.

Exam Topics

  • Architecture and Deployment10%
  • Policy Enforcement25%
  • Web Auth and Guest Services15%
  • Profiler15%
  • BYOD15%
  • Endpoint Compliance10%
  • Network Access Device Administration10%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated July 9, 2026 at 10:04 PM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Architecture and Deployment

In a Cisco ISE split-deployment model, which workload is divided between the nodes?

Explanation

Cisco ISE split deployments divide the authentication, authorization, and accounting (AAA) workload between the primary and secondary nodes, optimizing the AAA workflow while allowing either node to handle the full AAA workload if connectivity fails.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Architecture and Deployment

Which two features remain available when the primary admin node is down and the secondary admin node has not yet been promoted?

Choose two
Explanation

During the interval before secondary PAN promotion, Cisco ISE continues to support existing or new Active Directory user RADIUS authentication and posture. Hotspot is excluded as a device-registration flow; Guest AUP is unavailable; and BYOD onboarding with the internal CA requires an active primary PAN.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

Architecture and Deployment

How is redundancy for Policy Service Nodes achieved in a deployment?

Explanation

Cisco ISE achieves Policy Service Node redundancy by placing two or more PSNs in a node group. Group members detect peer failures and a surviving member can issue Change of Authorization requests to reset affected URL-redirected sessions, enabling clients to reconnect through an available PSN. Cisco ISE Network Deployments documentation

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Network Access Device Administration

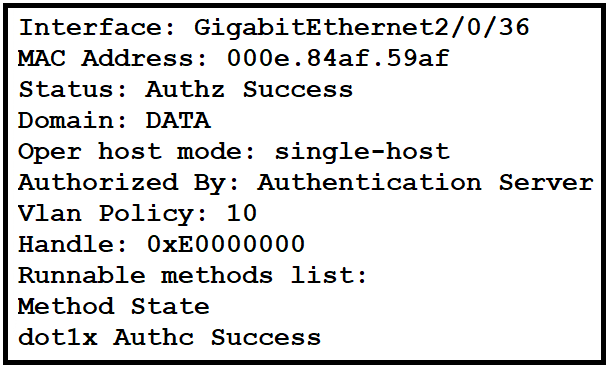
Which command shows all active 802.1X/MAB sessions on the switch ports of a Cisco Catalyst switch?

Explanation

show authentication sessions displays all current Auth Manager sessions, including sessions authenticated through 802.1X (dot1x) and MAC Authentication Bypass (mab). No interface qualifier is used when all switch-port sessions are required.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Architecture and Deployment

What is the purpose of the ip http server command on a switch?

Explanation

The ip http server command enables the HTTP server, which web-based authentication uses to communicate with and redirect clients for authentication. HTTPS requires ip http secure-server; 802.1X and MAB are enabled with separate authentication configuration.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home