About the Exam

This 120-minute Cisco exam covers security concepts, security monitoring, host-based analysis, network intrusion analysis, and security policies and procedures. It is the core exam for Cisco’s Cybersecurity Associate certification. Passing demonstrates knowledge and skills aligned to entry-level cybersecurity operations work.

Exam Topics

  • Security Concepts20%
  • Security Monitoring25%
  • Host-Based Analysis20%
  • Network Intrusion Analysis20%
  • Security Policies and Procedures15%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated July 11, 2026 at 7:48 PM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Network Intrusion Analysis
Question Image

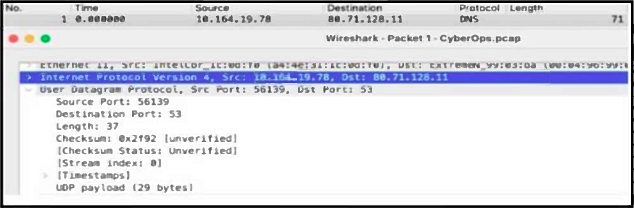
Refer to the exhibit. What type of activity is occurring in the network?

Explanation

DNS uses UDP port 53 for typical queries. UDP traffic directed to destination port 53 and identified as DNS is consistent with a DNS flood, in which a target receives a high volume of DNS requests.

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Host-Based Analysis

Question Image

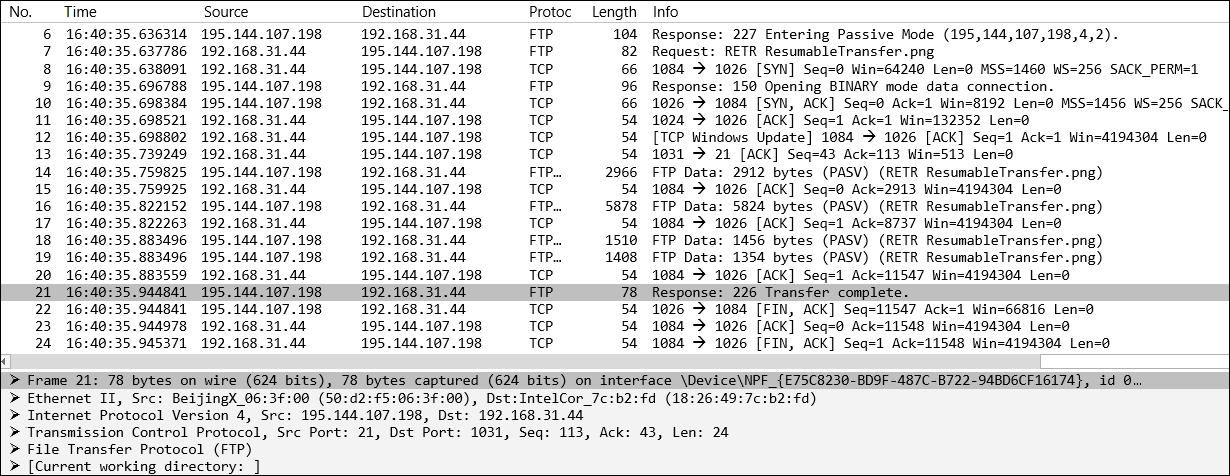
Refer to the exhibit. Which frame numbers contain a file that can be extracted through a TCP stream in Wireshark?

Explanation

The transferred file payload is carried by the FTP Data packets in frames 14, 16, 18, and 19. TCP stream reassembly combines those payload-bearing segments into the file; the FTP control messages in frames 7 and 21 contain only the resume command and completion status.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ3

Security Concepts

Which open-source packet-capture tool is used on the Linux and Mac OS X operating systems?

Explanation

tcpdump is an open-source packet-capture utility for Unix-like platforms, including Linux and macOS. It captures and displays network packets from a command line.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Security Policies and Procedures

The SOC team has verified a potential indicator of compromise on an endpoint. The team has narrowed the executable file type down to a new trojan family.

According to the NIST Computer Security Incident Handling Guide, what is the next step for handling this event?

Explanation

NIST SP 800-61 Rev. 2 includes researching suspected malicious activity—such as consulting search engines and knowledge bases—during detection and analysis. Public information about the newly identified trojan family can establish its behavior and help determine the incident before prioritization or containment.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Network Intrusion Analysis

Question Image

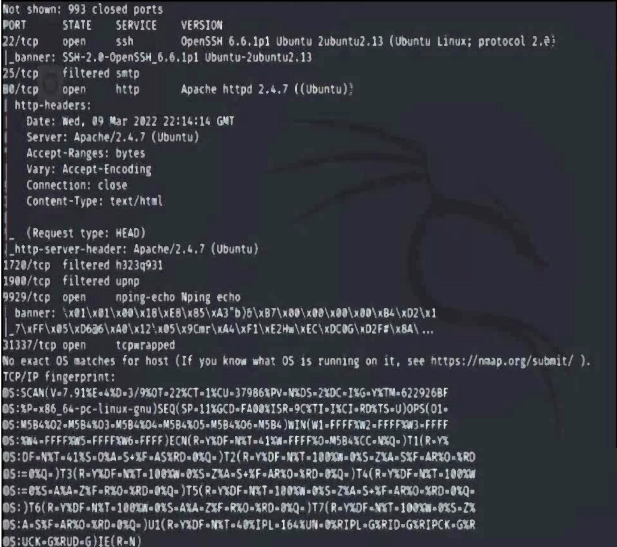
Refer to the exhibit. A penetration tester performs an Nmap scan against the company server to discover potential vulnerabilities and exploit them. Which two elements can the penetration tester identify from the scan results?
Choose two
Explanation

Open-port and version-detection results identify the listening services and applications, such as OpenSSH and Apache HTTP Server. The exposed SSH and HTTP services also reveal the server’s externally observable purpose and functionality: remote-access administration and web-service delivery. A port scan does not disclose local UIDs/group identifiers, a configured concurrent-connection limit, or server uptime.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home