QuestionQ23
VerifiedImplement and manage storageYour network has an on-premises Active Directory Domain Services (AD DS) domain.
The domain includes the identities in the following table.
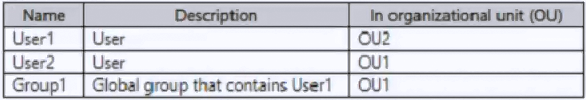
You have an Azure subscription containing a storage account named storage1. The file shares in storage1 use AD DS as the identity source, and the default share-level permissions are set to Enable permissions for all authenticated users and groups.
You create an Azure Files share named share1 with the roles shown in the following table.
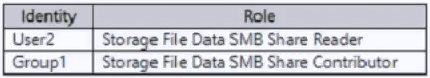
Your Microsoft Entra tenant contains a cloud-only user named User3.
You use Microsoft Entra Connect to synchronize OU1 from the AD DS domain to the Microsoft Entra tenant.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| User1 can access content in share1. | ||
| User2 can access content in share1. | ||
| User3 can access content in share1. |
Community Discussion