QuestionQ18

Security Engineering

After a cybersecurity incident, a security analyst was able to collect a binary that the attacker used on the compromised server. Then the analyst ran the following command:
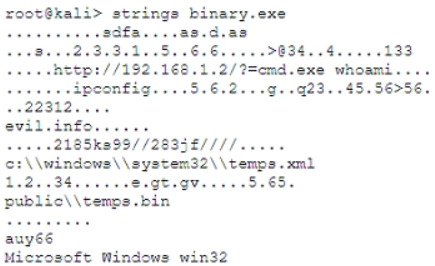
Question Image

Which of the following options describes what the analyst is trying to do?

Explanation

Running the strings command against the captured binary pulls out embedded plaintext artifacts such as IP addresses, URLs, domain names (e.g., evil.info), and file paths, all of which are indicators of compromise that help attribute and detect the malware elsewhere in the environment. This is basic static analysis for IoC extraction, not a debugger, sandbox replication, or timeline tool.

Community Discussion

No comments yet. Be the first to start the discussion!