QuestionQ17
Security EngineeringSIMULATION
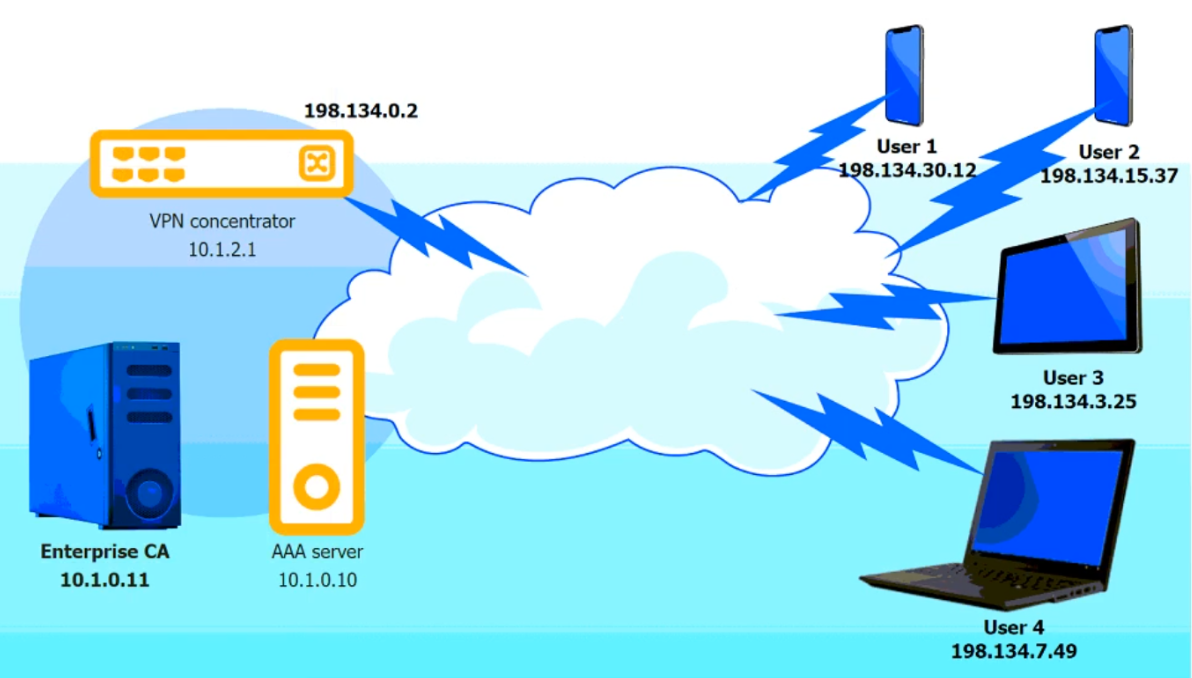
An IPSec solution is being deployed. The configuration files for both the VPN concentrator and the AAA server appear in the diagram.
Complete the configuration files to satisfy the following requirements:
- The EAP method must use mutual certificate-based authentication (with issued client certificates).
- The IKEv2 cipher suite must be configured to the most secure authenticated mode of operation.
- The secret must contain at least one uppercase character, one lowercase character, one numeric character, and one special character, and must meet a minimum length requirement of eight characters.
Select
VPN concentrator ... re-eap { ... proposals = ... } ... plugins { eap-radius { ... secret = Str0ng@Key server = } } ... AAA server ... eap { default_eap_type = ... } ... ip addr = secret = Str0ng@Key require_message_authenticator = yes } ...
Community Discussion