QuestionQ30

Management and Operations
Question Image

Question Image

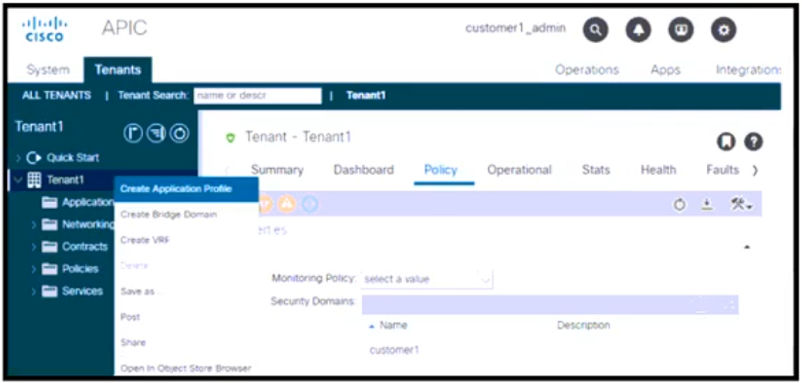
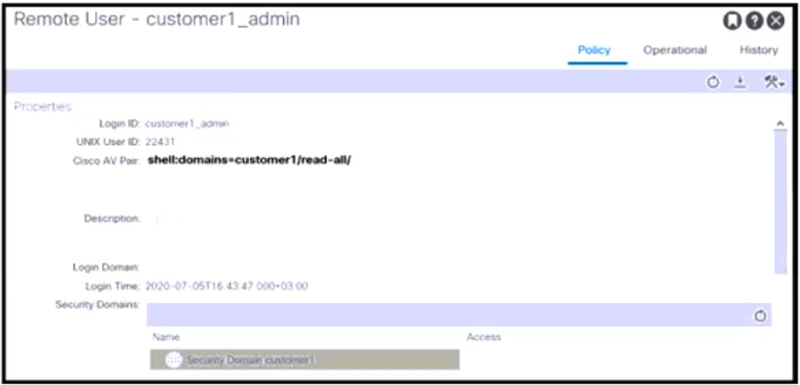
Refer to the exhibit. The Cisco ACI fabric has RADIUS realm configured as the default authentication method. The customer1_admin user has the read-all role configured but can still create new objects in Tenant1. Which Cisco AV pair must be used to correct the issue?

Explanation

Cisco APIC interprets shell:domains=<security-domain>/<write-roles>/<read-roles> such that a role in the middle field grants write access, while a role after // grants read-only access. shell:domains=customer1//admin places admin in the read-role field for the customer1 security domain, preventing creation of tenant objects.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!