User1 and User2 are new users, each granted a different functional role. User1 received IT_ANALYST_ROLE, and User2 received FIN_ANALYST_ROLE.
IT_ANALYST_ROLE
FIN_ANALYST_ROLE
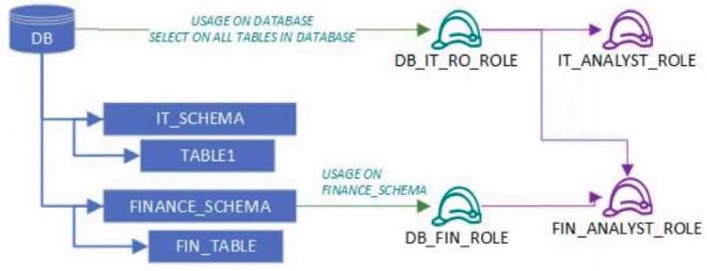
Review the following security design:
Which tables can each role read?
Accessing a Snowflake table requires privileges on its containing database and schema, in addition to SELECT on the table. IT_ANALYST_ROLE inherits database USAGE and table SELECT privileges but has no schema USAGE, so it cannot read any table. FIN_ANALYST_ROLE inherits the database access through the role hierarchy and has USAGE on FINANCE_SCHEMA plus SELECT on FIN_TABLE, allowing it to read the Finance table only.
SELECT
USAGE
FINANCE_SCHEMA
FIN_TABLE
Community Discussion