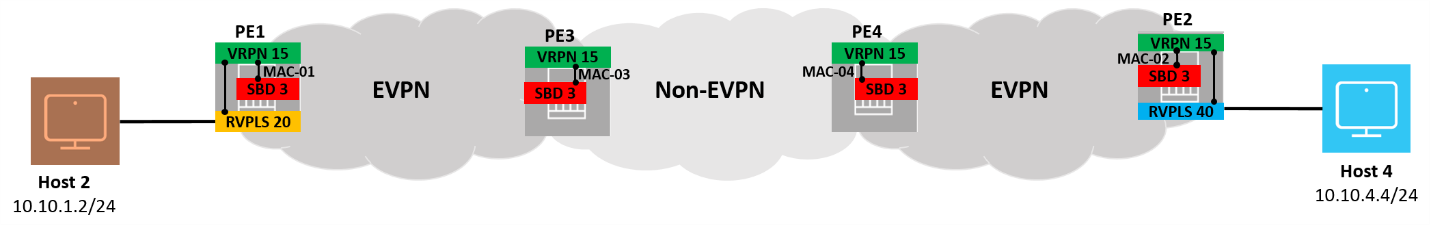
PE1 and PE3 belong to the same EVPN cloud, while PE3 and PE4 are connected only through a non-EVPN transport, over which VPRN 15 routes must be exchanged using the classic VPN-IPv4 (RFC 4364) address family rather than EVPN routes; PE4 and PE2 again belong to a separate EVPN cloud. Because PE1 and PE2 are not part of the same EVPN domain — they are separated by the intervening non-EVPN segment between PE3 and PE4 — there is no direct MP-BGP session carrying EVPN routes between PE1 and PE2. EVPN route exchange only occurs within each EVPN cloud (PE1–PE3 and PE4–PE2); the Supplementary Broadcast Domain (SBD) on the border PEs (PE3, PE4) is what stitches the EVPN and non-EVPN segments together by translating between EVPN MAC/IP routes and VPN-IPv4 routes. This makes the claim of a direct PE1–PE2 EVPN BGP session incorrect, while the other statements (VPN-IPv4 session between PE3 and PE4, overlay-index resolution to MAC-01 for the PE1-attached subnet, and transport-tunnel resolution toward PE4 for the PE2-attached subnet) are all consistent with the topology.
Community Discussion