QuestionQ72
VerifiedSecure, optimize, and deploy database solutionsFabrikam has a single Azure subscription in the East US 2 Azure region. The subscription contains an Azure SQL database named DB1. DB1 contains the following tables:
- Patients
- Employees
- Procedures
- Transactions
- UsefulPrompts
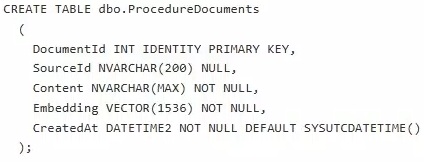
- ProcedureDocuments
A column master key is stored as a secret in Azure Key Vault.
An on-premises application named TransactionProcessing uses a hard-coded username and password in a connection string to access DB1.
Users report that updates to underlying data are sometimes inconsistent after the long-running stored procedure named sp_UpdateProcedureForPatient runs.
Fabrikam plans to manage every Azure SQL Database object change through source control in GitHub. Each pull request to production will be validated before it is merged. Deployments must use the Release configuration.
Fabrikam has these security requirements:
- TransactionProcessing must use a passwordless connection to DB1.
- The Employees table's TaxID and Salary columns must be encrypted at rest.
- Auditors must have a tamper-evident transaction history with cryptographic proof of employee-data changes.
Records accessed by sp_UpdateProcedureForPatient must not be changed by other transactions while that stored procedure is running.
Fabrikam has these AI-related requirements:
- Queries to ProcedureDocuments must use Reciprocal Rank Fusion (RRF).
- Users must be able to query DB1 using prompts in Copilot in Microsoft Fabric.
- UsefulPrompts will store prompts doctors can use to help diagnose patient illness by connecting to an Azure OpenAI endpoint.
Fabrikam has these development requirements:
- Retrieve all transactions for a specified patient between two dates, with a running total.
- Expose a Data API builder (DAB) configuration file that enables Azure services, through a REST API, to read Procedures without authentication; read and insert Transactions after authentication; and execute the sp_UpdateProcedurePatient stored procedure.
- Retrieve the names of patients who had medical procedures during the last 30 days.
- Store information for each medical procedure in a table for use with an LLM for user querying, with the following structure.
DAB
A DAB configuration file that fulfills the DB1 development requirements includes the following entities.
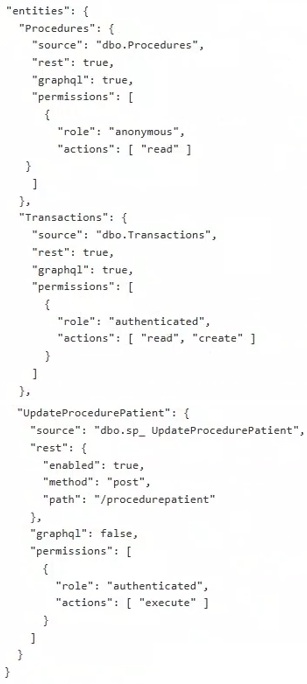
Evaluate the DAB configuration.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
| Statements | Yes | No |
|---|---|---|
| Applications can read data in the Procedures table without authentication. | ||
| Applications can read and update data in the Transactions table once authenticated. | ||
| Applications can execute the sp_UpdateProcedurePatient stored procedure. |
Community Discussion