QuestionQ14
Secure Windows Server on-premises and hybrid infrastructuresHOTSPOT
Your network has an on-premises Active Directory Domain Services (AD DS) domain. The domain includes the servers listed in the following table.
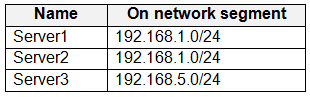
For each server, Windows Defender Firewall is set to allow communication only between servers on the same segment.
Server1 has this connection security rule:
- Name: Rule1
- Rule type: isolation
- Requirement: Require authentication for inbound connections and request authentication for outbound connections
- Authentication method: Computer (Kerberos V5)
- Profile: Domain, Private, Public
Server2 has no connection security rules.
Server3 has this connection security rule:
- Name: Rule3
- Rule type: Server-to-server
- Endpoints
- Computers in Endpoint 1: 192.168:5.0/24
- Computers in Endpoint 2: 192.168.1.0/24
- Requirement: Request authentication for inbound and outbound connections
- Authentication method: Computer (Kerberos V5)
- Profile: Domain, Private, Public
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| Server1 can initiate communication with Server2 successfully. | ||
| Server2 can initiate communication with Server3 successfully. | ||
| Server3 can initiate communication with Server1 successfully. |
Community Discussion