QuestionQ9
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeOverview
Fabrikam, Inc. is a manufacturing company with a main office in New York and a branch office in Seattle.
Existing Environment
On-premises Servers
The on-premises network includes servers that run Windows Server, as shown in the following table.
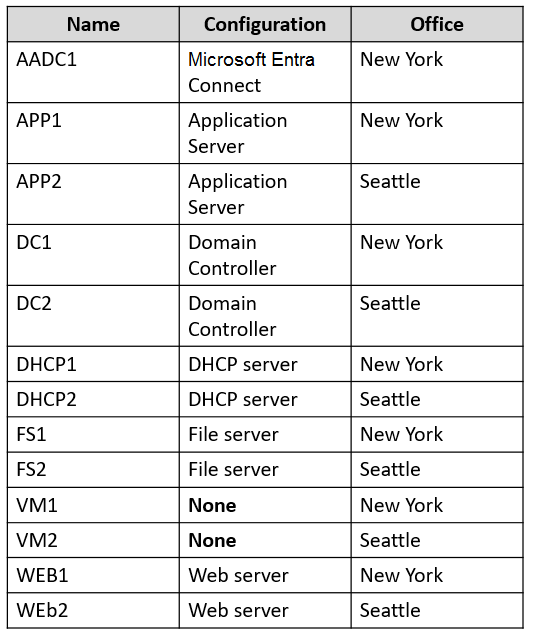
DC1 hosts all the operation master roles.
VM1 and VM2 are connected to the internet.
WEB1 and WEB2 run an Internet Information Services (IIS) web app named Webapp1.
On-premises Network
The New York and Seattle offices are connected by redundant WAN links.
Client computers in each office receive IP addresses from their local DHCP server.
DHCP1 contains a scope named Scope1 that has addresses for the New York office, and DHCP2 contains a scope named Scope2 that has addresses for the Seattle office.
Identity Infrastructure
The network contains a single on-premises Active Directory Domain Services (AD DS) domain named corp.fabrikam.com. Currently, all the service accounts use individual domain user accounts.
All domain controllers have the DNS Server role installed and host a copy of the Active Directory integrated DNS zone of corp.fabrikam.com.
The corp.fabrikam.com AD DS domain syncs with a Microsoft Entra tenant.
Group Policy Objects (GPOs)
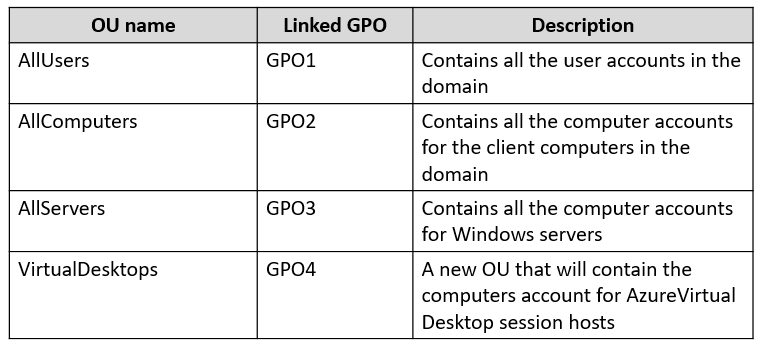
The corp.fabrikam.com domain contains the organizational units (OUs) and custom Group Policy Objects (GPOs) shown in the following table.
Requirements
Planned Changes
Fabrikam identifies the following planned changes:
- Create a single Azure subscription named
Sub1that will contain a single Azure virtual network namedVnet1. - Replace the WAN links between the Seattle and New York offices by using Azure Virtual WAN and FxpressRoute. Both on premises offices will be connected to
Vnet1by using ExpressRoute. - Create three Azure file shares named
newyorkfiles,seattlefiles, andcompanyfiles. - Create a domain controller named
dc3.corp.fabrikam.cominVnet1. - Deploy an Azure Virtual Desktop host pool to
Vnet1. The Azure Virtual Desktop session hosts will be hybrid Microsoft Entra joined. - License all servers for Microsoft Defender for servers.
- Use Azure Policy to enforce configuration management policies on the servers in Azure and on-premises.
Networking Requirements
Fabrikam identifies the following networking requirements:
- Implement Virtual WAN and ensure that all the network traffic between the sites uses Virtual WAN. All communications must occur over ExpressRoute.
- If a DHCP server fails, ensure that the client computers can continue to receive their dynamic IP address and renew their existing lease.
- Ensure that the resources in
Vnet1can resolve the names of the on-premises servers in thecorp.fabrikam.comdomain.
Security Requirements
Fabrikam identifies the following security requirements:
- Apply GPO4 to the Azure Virtual Desktop session hosts. Ensure that Azure Virtual Desktop user sessions lock after being idle for 10 minutes. Users must be able to control the lockout time manually from their client computer.
- Ensure that server administrators request approval before they can establish a Remote Desktop connection to an Azure virtual machine. If the request is approved, the connection must be established within two hours.
- Prevent user passwords from containing all or part of words that are based on the company name, such as Fab, f@br1kAm or fabr!.
- Ensure that all instances of Webapp1 use the same service account. The password of the service account must change automatically every 30 days.
- Prevent domain controllers from directly contacting hosts on the internet.
File Sharing Requirements
You need to configure the synchronization of Azure files to meet the following requirements:
- Ensure that
seattlefilessyncs toFS2. - Ensure that
newyorkfilessyncs toFS1. - Ensure that
companyfilessyncs to bothFS1andFS2.
Which implementation should be used to deploy DC3?
Community Discussion