QuestionQ83
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeYour network contains an Active Directory Domain Services (AD DS) forest named adatum.com. Adatum.com contains the users displayed in the following table.
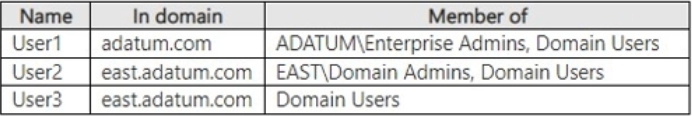
You deploy a workgroup server named RODC1 that runs Windows Server. RODC1 has a user named User4 who is a member of the local Administrators group.
You precreate a read-only domain controller (RODC) account named RODC1 in east.adatum.com and delegate RODC installation and administration permissions to User3.
You sign in to RODC1 as User4.
Which credentials can you use to promote RODC1 to an RODC in east.adatum.com?
Community Discussion