QuestionQ25
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeHOTSPOT
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com.
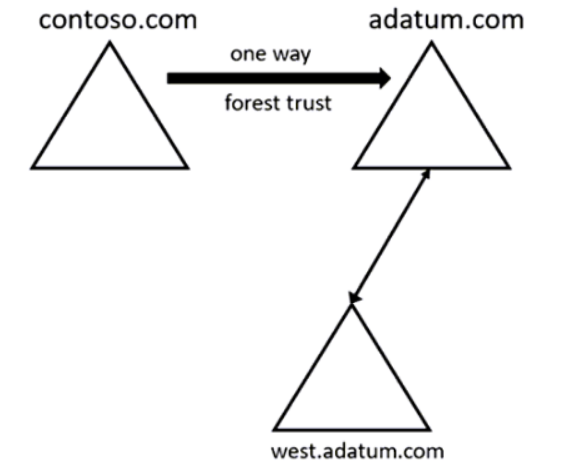
A partner company, ADatum Corporation, has an AD DS forest named adatum.com. You configure the trust relationship shown in the following exhibit.
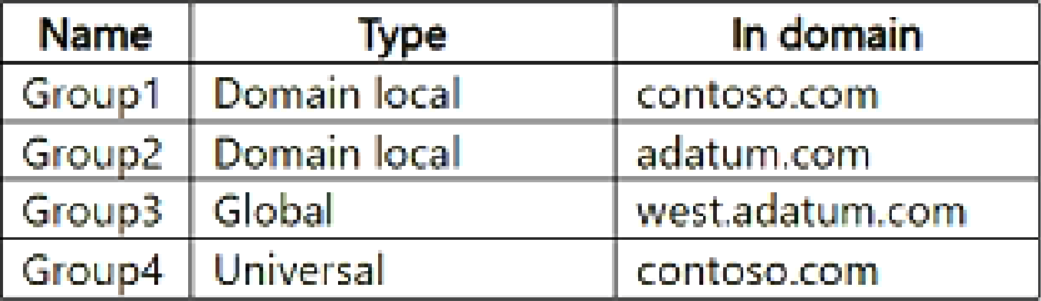
The forests contain the groups shown in the following table.
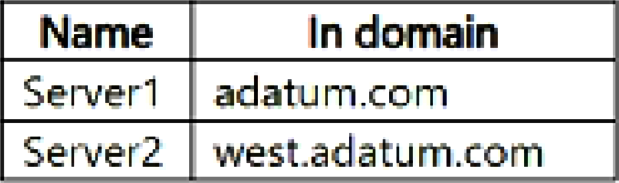
The ADatum domains contain the member servers shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| Group2 can be assigned permissions for the resources on Server2. | ||
| Group3 can be added as a member of Group1. | ||
| Group4 can be assigned permissions for the resources on Server1. |
Community Discussion