QuestionQ233
VerifiedAdministración de servicios de archivos y almacenamientoYour network has an Active Directory Domain Services (AD DS) domain named adatum.com. The domain includes a server named Server1 and the users shown in the following table.
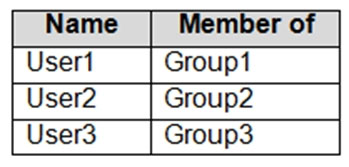
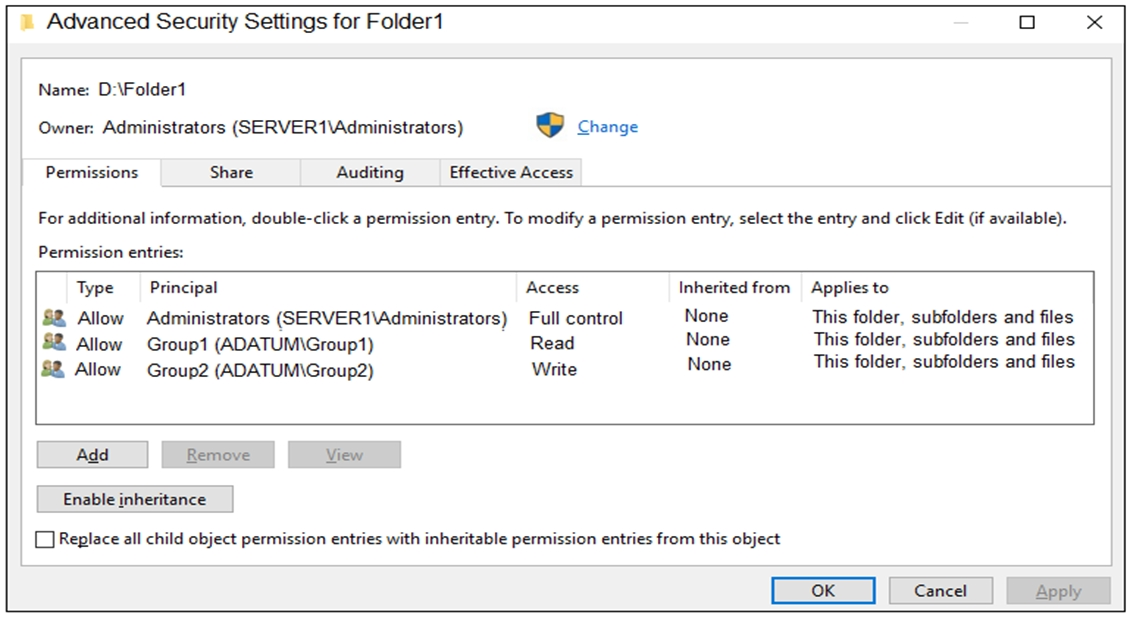
Server1 has a folder named D:\Folder1. The advanced security settings for Folder1 are configured as shown in the Permissions exhibit. (Select the Permissions tab.)
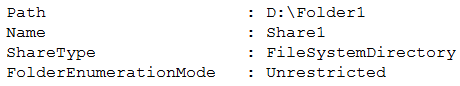
Folder1 is shared with the following configuration:
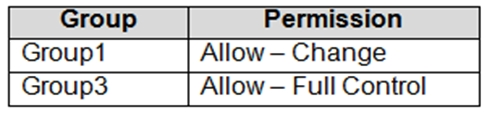
The share permissions for Share1 are shown in the following table.
For each statement, select Yes if it is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| User1 can read the files in Share1. | ||
| User3 can delete files in Share1. | ||
| If User2 connects to \Server1.adatum.com from File Explorer, Share1 will be listed. |
Community Discussion