QuestionQ154
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeYour network has an on-premises Active Directory Domain Services (AD DS) domain named contoso.com that synchronizes with an Azure AD tenant. The tenant includes a group named Group1 and the users in the following table.
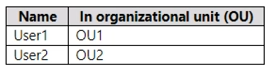
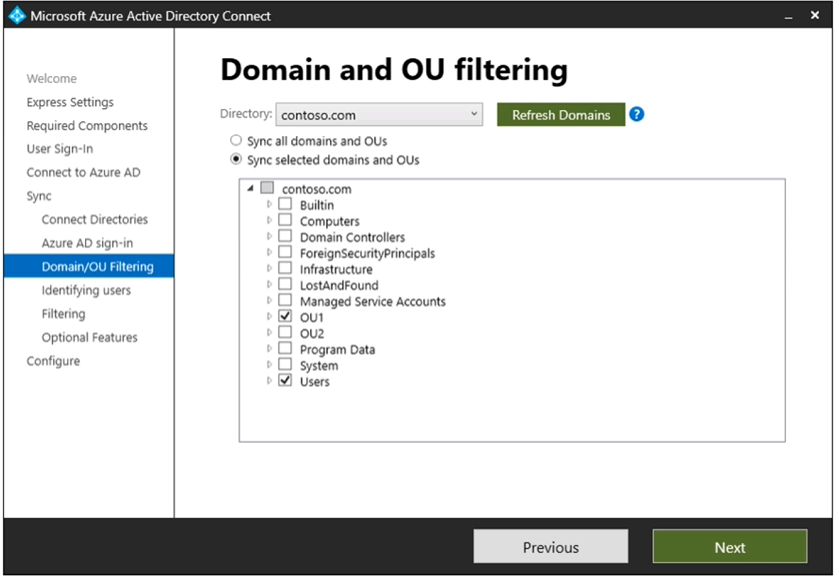
Azure AD Connect Domain/OU filtering is configured as shown in the Filtering exhibit. (Select the Filtering tab.)
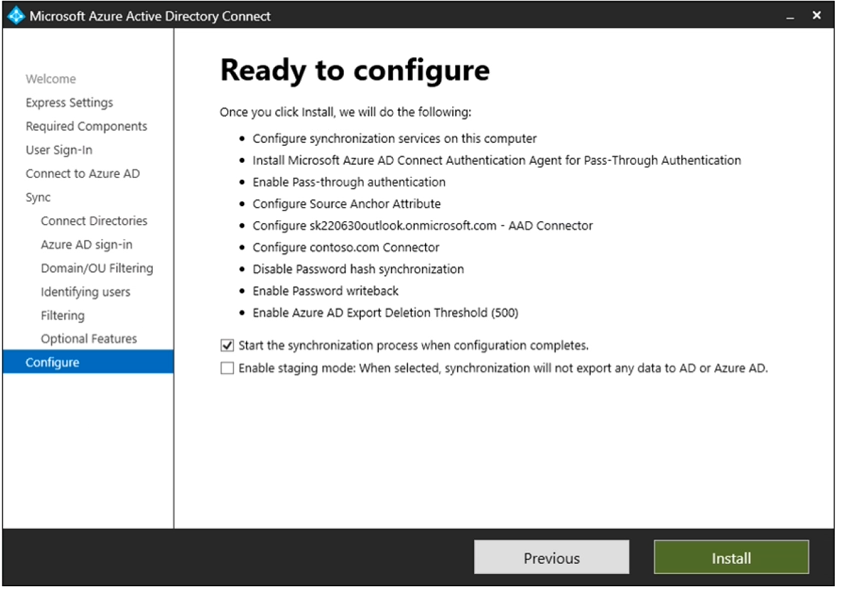
Review the Azure AD Connect configuration shown in the Configure exhibit. (Select the Configure tab.)
For each statement, select Yes when it is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| User1 can use self-service password reset (SSPR) to reset his password. | ||
| If User1 connects to Microsoft Exchange Online, an on-premises domain controller provides authentication. | ||
| You can add User2 to Group1 as a member. |
Community Discussion