QuestionQ111
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeYour network contains two Active Directory Domain Services (AD DS) forests, as shown in the following table.
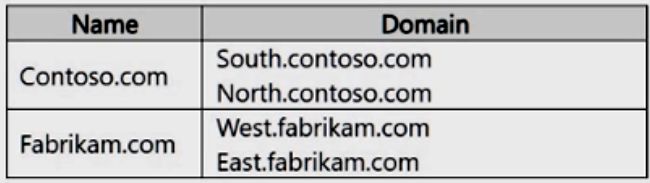
West.fabrikam.com contains a file server named Fileserver01. South.contoso.com has a global group named Group1.
You need to ensure that Group1 members can access a share on Fileserver01. The solution must prevent users in the fabrikam.com forest from accessing resources in south.contoso.com.
Which type of trust should you implement?
Community Discussion