QuestionQ1
VerifiedImplementación y administración de Active Directory Domain Services (AD DS) en entornos locales y en la nubeYour network has an on-premises Active Directory Domain Services (AD DS) domain. The domain includes a user named User1 and the servers shown in the following table.
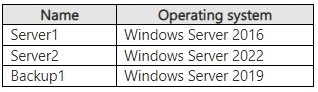
User1 belongs to the Protected Users security group.
User1 performs these actions:
- From Server1, establishes a remote PowerShell session to Server2.
- From the PowerShell session on Server2, tries to access a resource on Backup1.
The attempt to access the resource on Backup1 is denied.
You need to ensure that User1 can access the resources on Backup1 by using the PowerShell session on Server2. The solution must adhere to the principle of least privilege and minimize administrative effort.
What should you configure?
Community Discussion