QuestionQ78
VerifiedSecure networkingYou have an Azure subscription that contains an Azure key vault named KeyVault1 and the virtual machines shown in the following table.
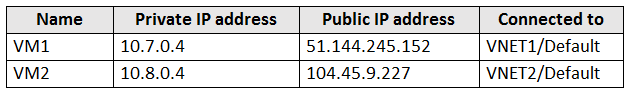
You configure the Key Vault access policy to enable access to Azure Disk Encryption for volume encryption. KeyVault1 is configured as shown in the following exhibit.
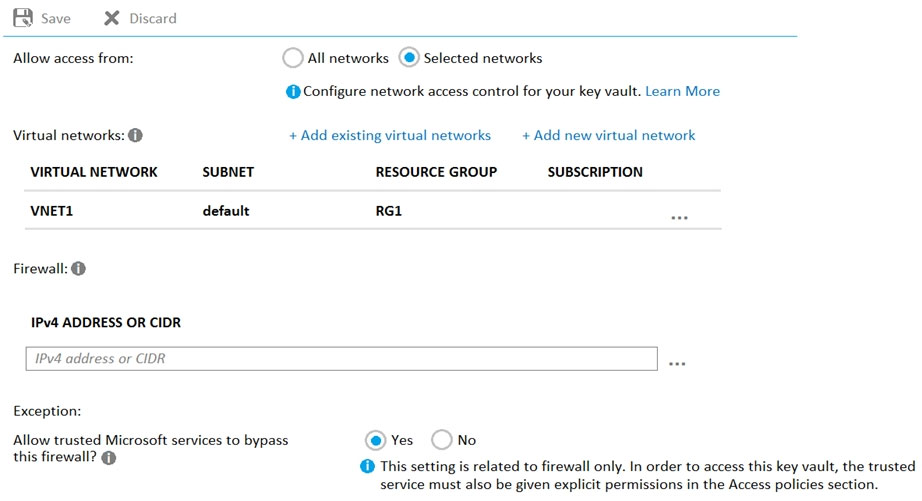
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| From VM1, users can manage the keys and secrets stored in KeyVault1. | ||
| From VM2, users can manage the keys and secrets stored in KeyVault1. | ||
| VM2 can use KeyVault1 for Azure Disk Encryption. |
Community Discussion