About the Exam

AZ-500 is Microsoft’s certification exam for Azure security engineers. It covers securing identity and access, networking, compute, storage, and databases, along with using Microsoft Defender for Cloud and Microsoft Sentinel. Passing demonstrates you can implement, manage, and monitor security for Azure, multi-cloud, and hybrid environments and apply Microsoft security best practices.

Exam Topics

  • Secure identity and access15–20%
  • Secure networking20–25%
  • Secure compute, storage, and databases20–25%
  • Secure Azure using Microsoft Defender for Cloud and Microsoft Sentinel30–35%

How to Use This Practice Exam

  1. Browse — Read each question, select your answer, and reveal the explanation.
  2. Exam Mode — Simulate real exam conditions with a timed session and score report.
  3. Learn Mode — Spaced repetition schedules questions you struggle with for long-term retention.

Download the Full Exam PDF

Get every question and answer in a clean, printable PDF built for offline study. Purchase once, keep permanent access, and re-download the latest version anytime.

Last updated July 12, 2026 at 7:40 AM

Topic filter
Retired questions
Question sort
Questions per page

QuestionQ1

Secure networking

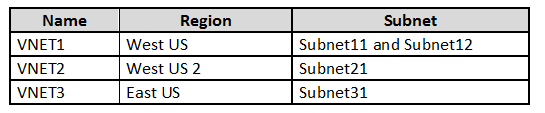
You have an Azure subscription that includes the virtual networks shown in the following table.
Question Image

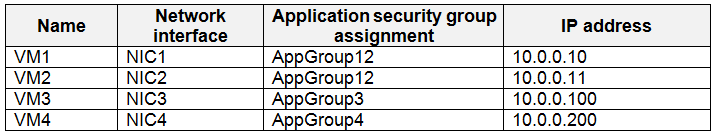
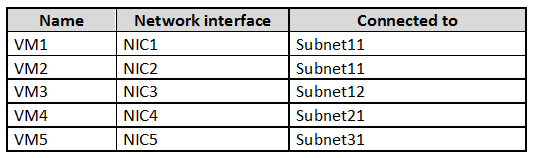
The subscription includes the virtual machines shown in the following table.
Question Image

You configure an application security group named ASG1 on NIC1.

On which other network interfaces can you configure ASG1?

Explanation

All network interfaces assigned to an Azure application security group must be in the same virtual network as the first interface assigned to that group. ASG1 is assigned to NIC1 in VNET1, so it can also be assigned to NIC2 and NIC3, which are in VNET1. NIC4 and NIC5 are in different virtual networks.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ2

Secure networking

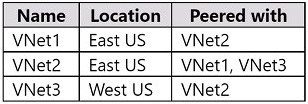
You have an Azure subscription containing the virtual networks shown in the following table.
Question Image

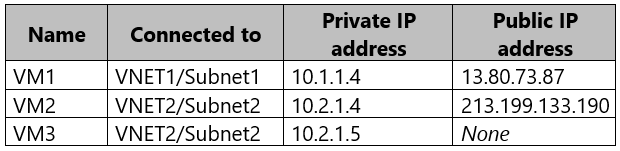
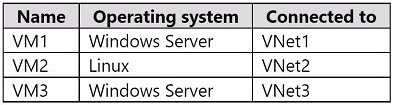
The subscription includes the virtual machines shown in the following table.
Question Image

All virtual machines have private IP addresses only.

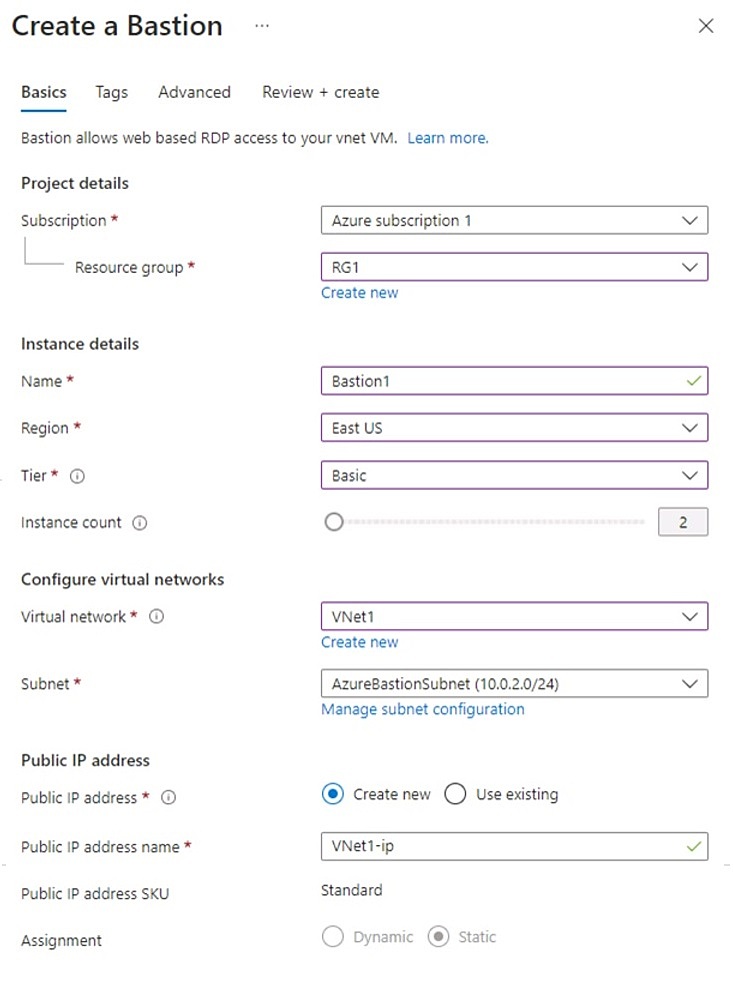
You deploy Azure Bastion to VNet1 as shown in the following exhibit.
Question Image

For each statement below, select Yes if it is true. Otherwise, select No.

Yes or No
StatementsYesNo
You can connect to VM1 through Bastion1 by using the Remote Desktop Connection client.
You can connect to VM2 through Bastion1 by using SSH.
You can connect to VM3 through Bastion1 by using the Azure portal.
Explanation

Azure Bastion Basic supports browser-based SSH connections to VMs in the same or directly peered virtual networks, but native RDP/SSH client connectivity requires the Standard or Premium SKU. VNet peering is nontransitive: a VNet1-to-VNet2 peering and a VNet2-to-VNet3 peering do not provide connectivity between VNet1 and VNet3. Azure Bastion SKU comparison, Azure Bastion overview

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ4

Secure identity and access

You have a Microsoft Entra tenant named contoso.com.

You plan to collaborate with a partner organization that has a Microsoft Entra tenant named fabrikam.com.

Fabrikam.com uses these identity providers:

  • Google Cloud Platform (GCP)
  • Microsoft accounts
  • Microsoft Entra ID

You need to configure the Cross-tenant access settings for B2B collaboration.

Which identity providers support cross-tenant access?

Explanation

Cross-tenant access settings control B2B collaboration with external Microsoft Entra organizations. Google and Microsoft accounts are supported as external identity providers for guest sign-in, but cross-tenant access settings apply only to Microsoft Entra tenants.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ5

Secure Azure using Microsoft Defender for Cloud and Microsoft Sentinel

After creating a new Azure subscription, you are tasked with ensuring that custom alert rules can be created in Azure Security Center.

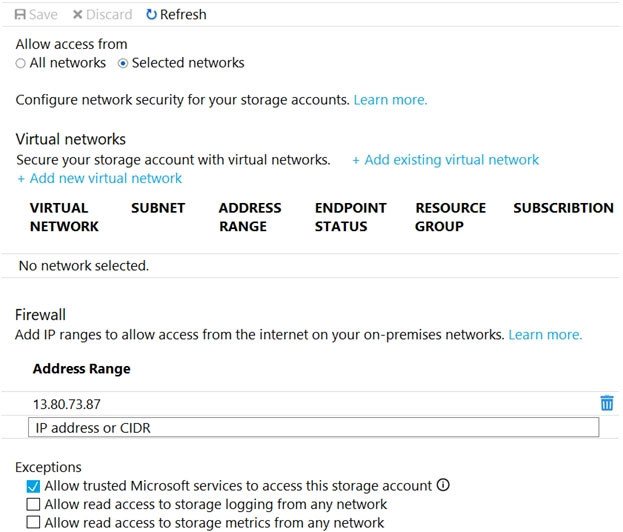
You have created an Azure Storage account.

Which action should you take?

Explanation

Custom log-based alert rules require a Log Analytics workspace as the target data store for collected logs and queries. Microsoft Defender for Cloud (formerly Azure Security Center) integrates with Log Analytics, and Azure Monitor creates custom log-search alert rules against that workspace.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!

QuestionQ6

Secure compute, storage, and databases

Your company uses an Azure Container Registry.

You must assign a user a role that permits uploading images to the Azure Container Registry. The assigned role must provide no more privileges than necessary.

Which of the following roles should you assign?
Explanation

The AcrPush role grants data-plane permission to push and pull container images and artifacts, without granting Azure resource-management permissions. AcrPull is limited to pulling images, while Contributor and Owner provide broader privileges than required.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!
Know a question that should be here? Contribute to this exam
Back home