QuestionQ69
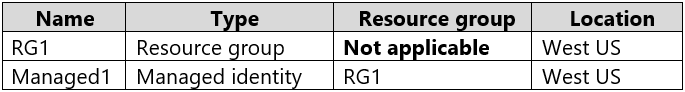
VerifiedSecure identity and accessYou have an Azure subscription containing the resources shown in the following table.
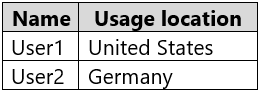
The subscription is linked to an Azure Active Directory (Azure AD) tenant containing the users shown in the following table.
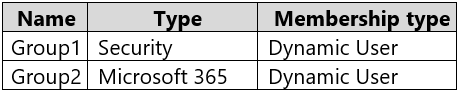
You create the groups shown in the following table.
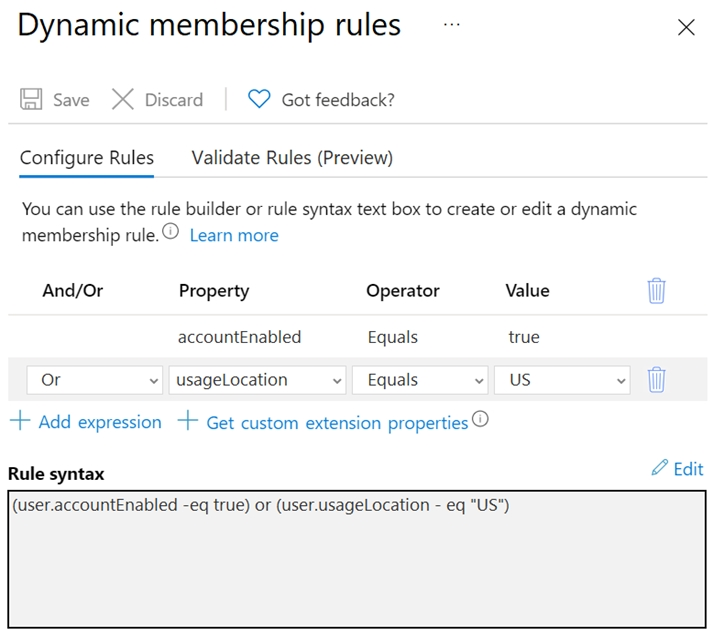
The membership rules for Group1 and Group2 are configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| User1 is a member of Group1 and Group2. | ||
| User2 is a member of Group2 only. | ||
| Managed1 is a member of Group1 and Group2. |
Community Discussion