QuestionQ65

VerifiedSecure compute, storage, and databases

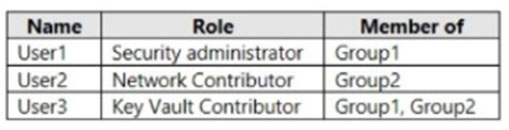
You have an Azure subscription linked to Azure Active Directory (Azure AD). The tenant contains the users listed in the following table.
Question Image

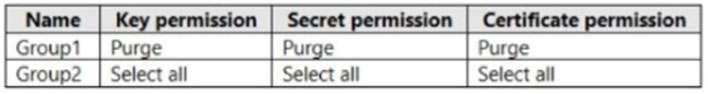
You have an Azure key vault named Vault1 with Purge protection set to Disable. Vault1 has the access policies shown in the following table.
Question Image

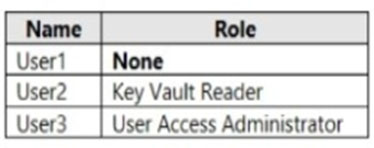
You create the role assignments for Vault1 shown in the following table.
Question Image

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

Yes or No
StatementsYesNo
User1 can set Purge protection to Enable for Vault1.
User2 can configure firewalls and virtual networks for Vault1.
User3 can add access policies to Vault1.
Explanation

Azure Key Vault separates a control plane (create/delete vaults, set access policies, configure network rules, and other vault properties such as purge protection) from a data plane (working with keys, secrets, and certificates). The control plane is authorized exclusively through Azure RBAC, while access policies (or RBAC data actions) govern only the data plane. The built-in Key Vault Contributor role grants control-plane management of a vault, including the ability to set access policies, without granting data-plane access to keys, secrets, or certificates - unlike Key Vault Reader, Network Contributor, or an Azure AD role such as Security administrator, none of which include the Microsoft.KeyVault/vaults/write permission needed for vault property changes like purge protection or network configuration.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!