QuestionQ18
VerifiedSecure identity and accessYou have the Azure resource hierarchy shown in the following exhibit.
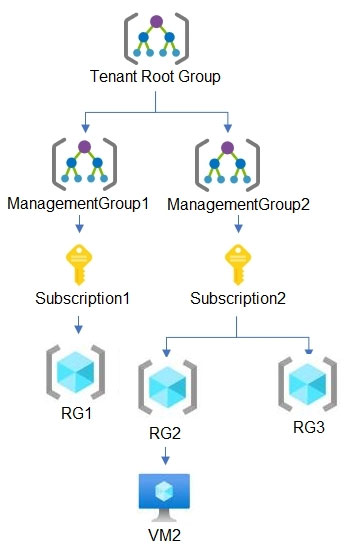
RG1, RG2, and RG3 are resource groups. RG2 contains a virtual machine named VM2. You assign Azure role-based access control (RBAC) roles to the users shown in the following table.
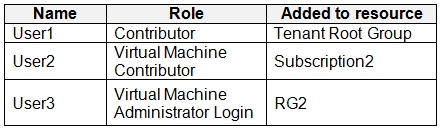
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| User1 can deploy virtual machines to RG1. | ||
| User2 can delete VM2. | ||
| User3 can reset the password of the built-in Administrator account of VM2. |
Community Discussion