QuestionQ79
VerifiedImplement and manage storageADatum Corporation is a consulting firm with its main office in Montreal and branch offices in Seattle and New York.
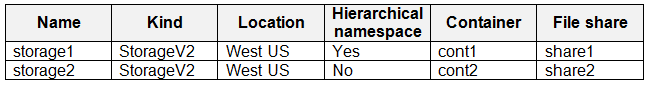
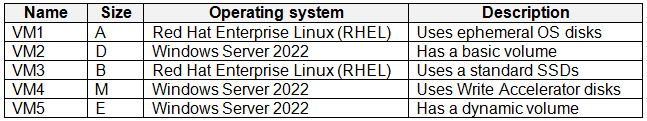
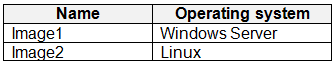
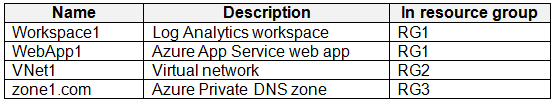
The Azure subscription contains RG1, RG2, and RG3. The storage accounts, virtual machines, container-registry images, and resources are shown below.
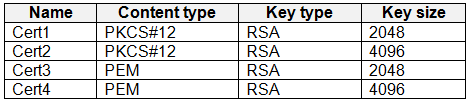
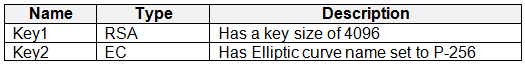
The subscription contains an Azure key vault named Vault1. Its certificates and keys are shown below.
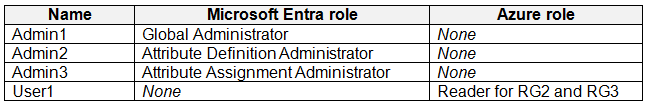
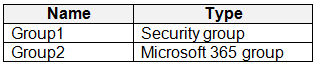
The linked Microsoft Entra tenant, adatum.com, contains the following users and groups.
ADatum plans to configure DCR1 to collect only system events with event ID 4648 from VM2 and VM4; create cont2 in storage1 with Stored1, Stored2, and Stored3 stored access policies and a legal hold for immutable blob storage; use directories whenever possible; grant User1 the permissions required to link Zone1 to VNet1; assign Attribute1 to supported adatum.com resources; create Scope1 in storage2; and deploy new containers using Image1 or Image2.
Technical requirements include TLS for WebApp1, least privilege, permissions only at the required scope, use of Scope1 to encrypt storage services, Azure Backup for cont1 and share1 as frequently as possible, and encryption at host with customer-managed keys (disk encryption set) whenever possible.
You implement the planned changes for cont2.
What is the maximum number of additional access policies that you can create for cont2?
Community Discussion