QuestionQ58

VerifiedImplement and manage virtual networking

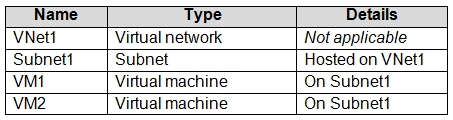
You have an Azure subscription that contains the resources in the following table.
Question Image

VM1 and VM2 are deployed from the same template and host line-of-business applications.

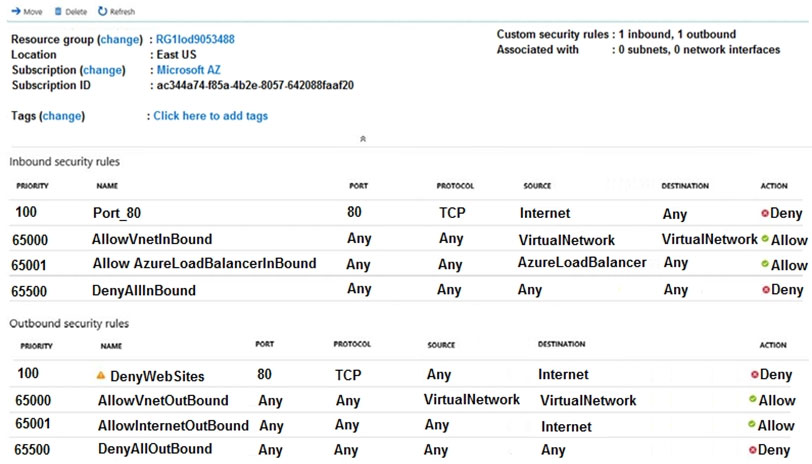
You configure the network security group (NSG) shown in the exhibit.
Question Image

You need to prevent users of VM1 and VM2 from accessing websites on the Internet over TCP port 80.

What should you do?

Explanation

In Azure, blocking users on virtual machines from reaching websites over TCP port 80 requires an outbound NSG rule that denies destination Internet on port 80, and that NSG must be associated with the subnet or the VMs' network interfaces for the rule to take effect. The configured DenyWebSites outbound rule already matches that requirement, but because the NSG is not associated with any subnet or NIC, it is not applied. Associating the NSG to Subnet1 applies the deny rule to both VM1 and VM2 because both virtual machines are deployed in that subnet. Official Microsoft documentation states that NSG rules filter inbound and outbound traffic only for associated subnets or network interfaces.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!