QuestionQ48

VerifiedImplement and manage storage

You have an Azure subscription that contains the storage accounts shown in the following table.
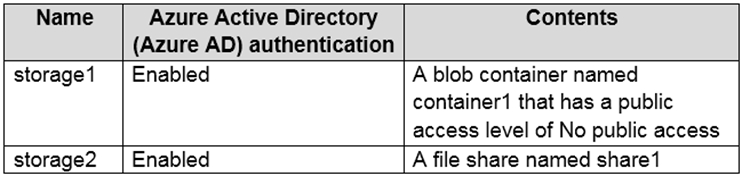
Question Image

You plan to use AzCopy to copy a blob from container1 directly to share1.

You need to identify which authentication method to use when you use AzCopy.

Your account has the Contributor role on both storage accounts but no data-plane role assignments (such as the Storage Blob Data or Storage File Data Privileged roles), and you must not create any additional role assignments.

What should you identify for each account?

Each method may be used once, more than once, or not at all.

Drag & Drop
storage1:
storage2:
Explanation

AzCopy authorizes requests with either Microsoft Entra ID (OAuth) or a SAS token. It does not take a storage account access key directly for Blob Storage or Azure Files. Current AzCopy supports Microsoft Entra ID for an Azure Blob source copied to an Azure Files SMB destination, but only if the signed-in identity holds data-plane roles, for example Storage Blob Data Reader on storage1 and Storage File Data Privileged Contributor on storage2. Your account has none and you can't add any, so OAuth won't work. Anonymous is ruled out because container1's access level is No public access. A SAS token, signed with the account key that the Contributor role can list, works for both storage1 (the source container) and storage2 (the destination share).

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!