QuestionQ272
VerifiedImplement and manage virtual networkingYou have a virtual network named VNET1 that contains the subnets shown in the following table:
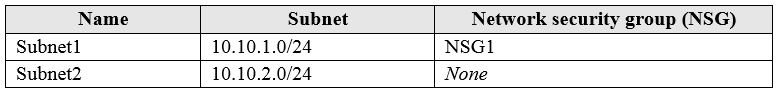
You have Azure virtual machines that have the network configurations shown in the following table:
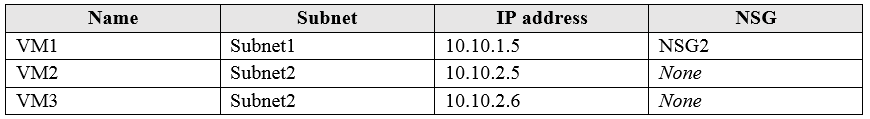
For NSG1, you create the inbound security rule shown in the following table:

For NSG2, you create the inbound security rule shown in the following table:

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Yes or No
| Statements | Yes | No |
|---|---|---|
| VM2 can connect to the TCP port 1433 services on VM1. | ||
| VM1 can connect to the TCP port 1433 services on VM2. | ||
| VM2 can connect to the TCP port 1433 services on VM3. |
Community Discussion