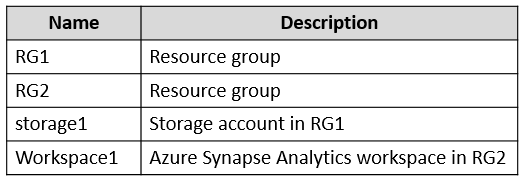
Workspace1 needs a data-plane role on the blob containers in storage1. Storage Blob Data Contributor grants read, write and delete access to Azure Storage containers and blobs directly through Azure RBAC, and nothing more, so it follows least privilege. Contributor, Storage Account Contributor and Reader and Data Access have no blob data actions. They reach the data only indirectly through the storage account keys (Shared Key authorization): Storage Account Contributor provides access to the account key, Reader and Data Access allows read/write access to all data in the account via the account keys, and Contributor can manage the whole account, including listing its keys. That is far broader than the required access to the container data.
Community Discussion