QuestionQ263

VerifiedManage Azure identities and governance

You have an Azure subscription named Sub1 that contains the Azure resources shown in the following table.
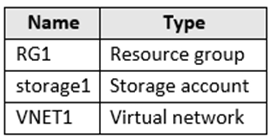
Question Image

You assign an Azure Policy with the following settings:

  • Scope: Sub1
  • Exclusions: Sub1/RG1/VNET1
  • Policy definition: Append a tag and its value to resources
  • Policy enforcement: Enabled
  • Tag name: Tag4
  • Tag value: value4

You assign tags to the resources as shown in the following table.
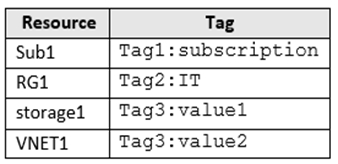
Question Image

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

Yes or No
StatementsYesNo
RG1 has the Tag2:IT tag assigned only
Storage1 has the Tag1:subscription, Tag2:IT, Tag3:value1, and Tag4:value4 tags assigned.
VNET1 has the Tag2:IT and Tag3:value2 tags assigned only
Explanation

The built-in definition Append a tag and its value to resources uses Indexed mode, and Microsoft documents that it does not apply to resource groups (a separate built-in, Append a tag and its value to resource groups, exists for that). RG1 is therefore never given Tag4 and keeps only the tag you assigned, Tag2:IT, so the first statement is true. storage1 is in scope and not excluded. Assigning Tag3:value1 is an update, which triggers the append effect, so storage1 ends up with Tag3:value1 and Tag4:value4. Tags aren't inherited from the subscription (Tag1) or the resource group (Tag2), so the second statement is false. VNET1 is excluded from the assignment, so it gets no Tag4, and it doesn't inherit Tag2:IT from RG1. It has only Tag3:value2, so the third statement is false.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!