QuestionQ211

VerifiedManage Azure identities and governance

You have the following custom role-based access control (RBAC) role.
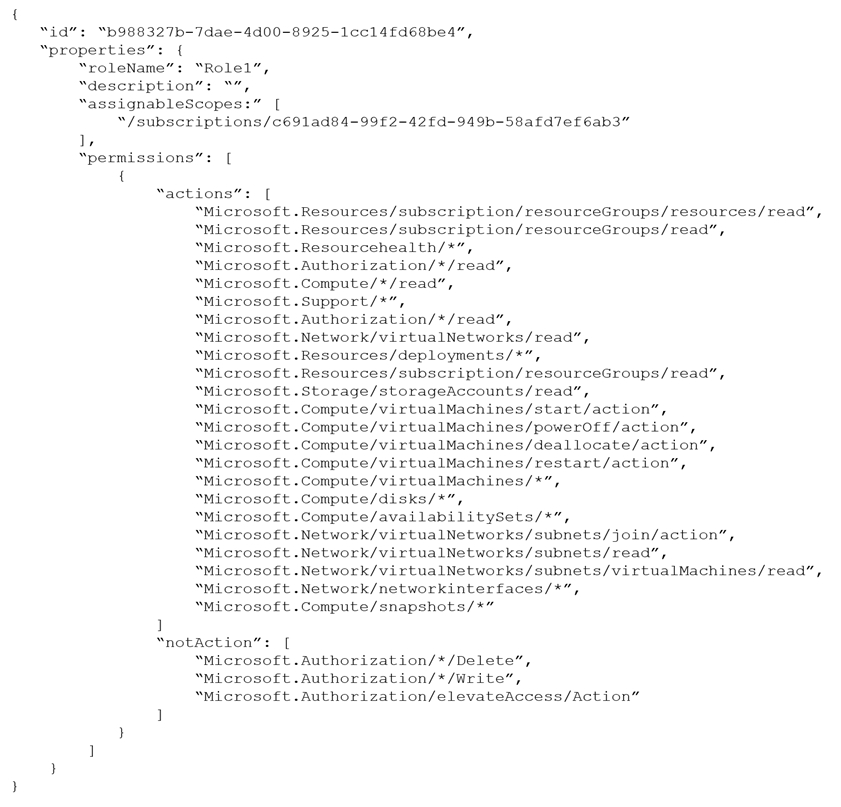
Question Image

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

Yes or No
StatementsYesNo
Users that are assigned Role1 can assign Role1 to users.
Users that are assigned Role1 can deploy new virtual machines.
Users that are assigned Role1 can set a static IP address on a virtual machine.
Explanation

Azure RBAC custom-role permissions are the effective Actions minus NotActions. This role allows only Microsoft.Authorization/*/read and explicitly excludes Microsoft.Authorization/*/Write and Microsoft.Authorization/*/Delete, so it cannot create role assignments and cannot assign Role1 to other users. It does allow VM deployment because it includes broad compute permissions such as Microsoft.Compute/virtualMachines/*, disk and availability set permissions, deployment permissions, and the network permissions needed to attach a NIC and join a subnet. A static IP address for an Azure VM is configured on the VM's network interface IP configuration, and the role includes Microsoft.Network/networkInterfaces/*, which permits changing that NIC configuration.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!