QuestionQ195

VerifiedManage Azure identities and governance

You have two Azure subscriptions named Sub1 and Sub2. Sub1 is in a management group named MG1. Sub2 is in a management group named MG2.

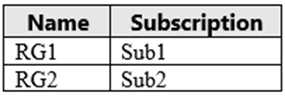
You have the resource groups shown in the following table.
Question Image

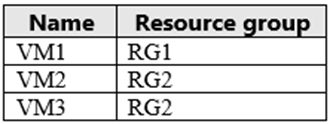
You have the virtual machines shown in the following table.
Question Image

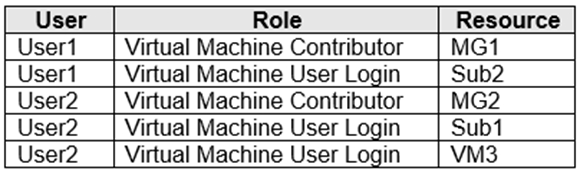
You assign roles to users as shown in the following table.
Question Image

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

Yes or No
StatementsYesNo
User1 can sign in to VM1.
User2 can manage disks and disk snapshots of VM1.
User2 can manage disks and disk snapshots of VM3.
Explanation

Azure RBAC role assignments are inherited down the resource hierarchy from management group to subscription to resource group to resource. Virtual Machine User Login grants only the data-plane sign-in action and no management rights, while Virtual Machine Contributor grants control-plane management of virtual machines and of the Microsoft.Compute/disks resource type (create, read, delete) but contains no Microsoft.Compute/snapshots actions, so it cannot manage disk snapshots. VM1 sits in RG1/Sub1/MG1, where only User1's Virtual Machine Contributor (assigned at MG1) applies, and that role has no DataActions, so User1 cannot sign in to VM1. For VM1, User2 only reaches it through the Sub1-scoped Virtual Machine User Login, which permits sign-in only, not disk management. VM3 sits in RG2/Sub2/MG2, where User2's Virtual Machine Contributor (assigned at MG2) applies and lets User2 manage VM3's disks, but since that role contains no snapshot-related permissions, User2 still cannot manage VM3's disk snapshots.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!