QuestionQ7

Identity-Aware Security Policies

Question Image

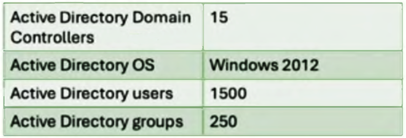
You are asked to configure your company’s SRX Series device to use identity-aware security policies. Information about your Active Directory network is shown in the exhibit.

In this scenario, why must you configure JIMS rather than Active Directory as the identity source?

Explanation

An SRX firewall using Active Directory directly as its identity source supports a maximum of 10 domain controllers on the higher-capacity supported platforms. With 15 domain controllers, the deployment exceeds that limit. JIMS is intended to collect and maintain identity data from larger, distributed Active Directory environments and supports many more event-log sources.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!