QuestionQ18
Intrusion Detection and Prevention (IDP)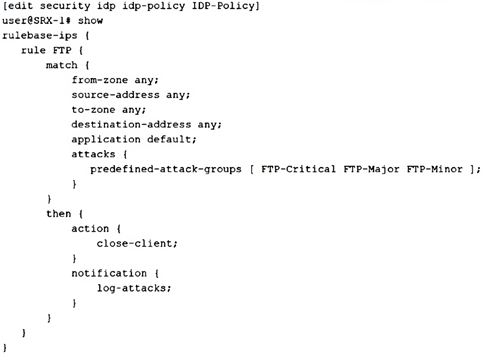
You want to add a custom attack object named Custom-FTP-Attack and configure the action to drop the packet. Referring to the exhibit, which changes would you make?
You want to add a custom attack object named Custom-FTP-Attack and configure the action to drop the packet. Referring to the exhibit, which changes would you make?
Community Discussion