QuestionQ11

VerifiedAnalyze

A hospital uses an AOS-10 architecture managed through HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways with Security licenses at every clinic. The gateways run IDS/IPS in IDS mode.

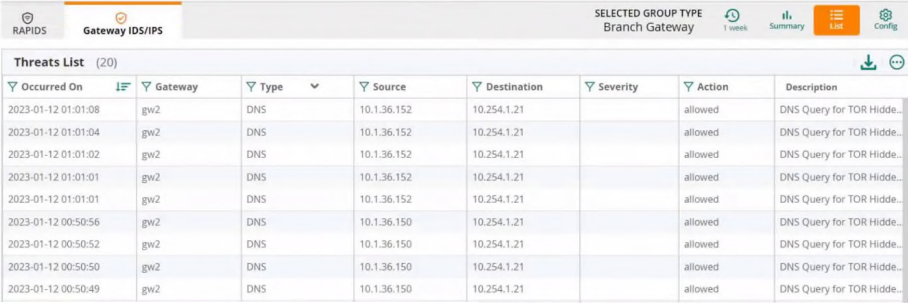
The Security Dashboard displays several recent events with the same signature, as shown below:
Question Image

Refer to the scenario.

Which action could provide valuable context about the incident?

Explanation

Gateway IDS/IPS identifies threats in traffic flows from hosts connected to the gateways. Reviewing the HPE Aruba Networking Central client profile for each source identifies the endpoint’s device category and OS family, helping determine whether the repeated DNS activity is expected for that type of client or requires investigation. RAPIDS and AP-specific user or firewall information address wireless AP/rogue-device context rather than the gateway-detected traffic source.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!