QuestionQ17

VerifiedIntegrating applications with Google Cloud services

You are attempting to connect to your Google Kubernetes Engine (GKE) cluster with kubectl from Cloud Shell. You deployed the GKE cluster with a public endpoint. From Cloud Shell, you run this command:
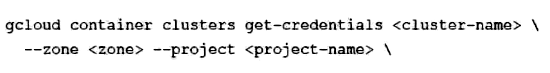
Question Image

You observe that kubectl commands time out without producing an error message. What is the most likely cause?

Explanation

GKE control-plane authorized networks restrict access to an IP-based public endpoint by source IP address. If Cloud Shell’s outgoing external IP address is not included in the cluster’s authorized-network CIDR ranges, requests to the Kubernetes control plane cannot connect and can time out. IAM or Kubernetes RBAC authorization failures would instead occur after connectivity is established and return an authorization-related error.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!