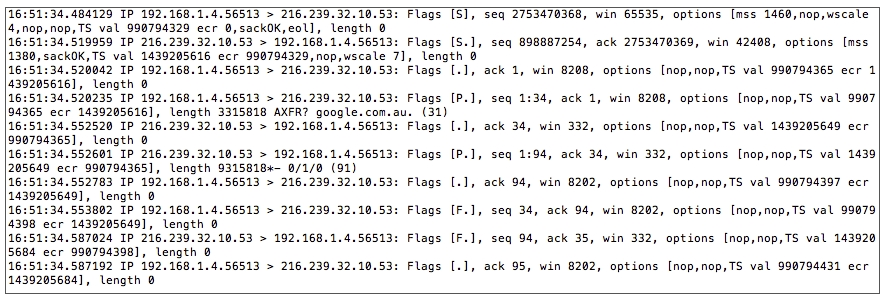
QuestionQ152Verified/Network and Log InvestigationsCopy linkReport a problemAsk AstroTutorSave questionBased on the tcpdump output below, what is an attacker trying to do? AUse a web crawlerBUse a search engineCRecord lookup (less than 512 bytes)DZone transferEWhois lookupShow AnswerAnswerExplanationA DNS zone transfer uses TCP port 53 to request and receive DNS zone data. The TCP handshake, data exchange, and connection close on port 53 are consistent with a zone-transfer attempt rather than a normal small DNS lookup.Show comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion