QuestionQ86
VerifiedIdentify and Resolve LTM Device Issues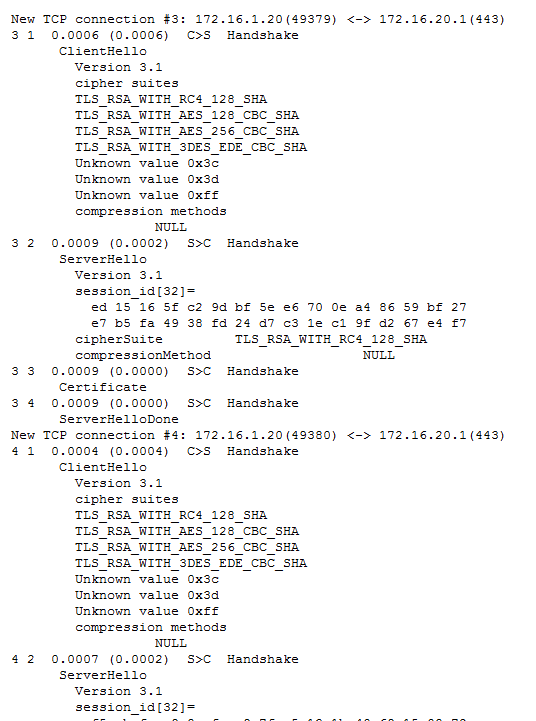
Refer to the exhibits.
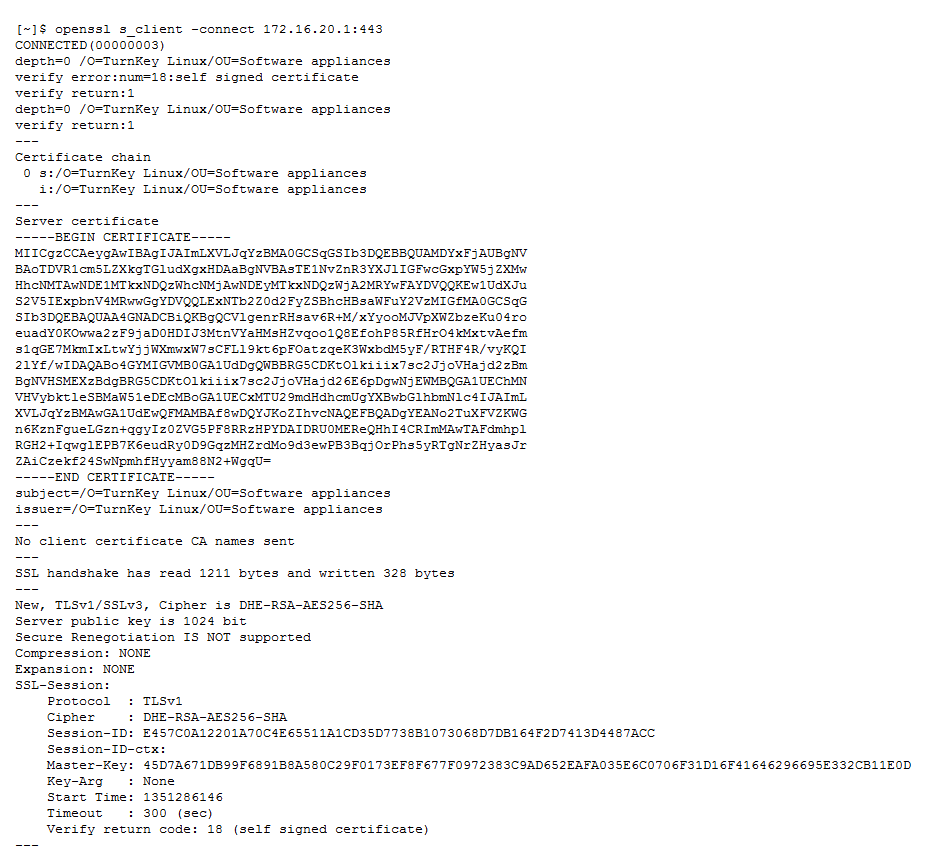
After upgrading LTM from v10 to v11, users cannot connect to an application. The virtual server uses a client SSL profile to re-terminate SSL for payload inspection, while a server SSL profile re-encrypts the request.
A client-side ssldump showed no differences between traffic sent directly to the server and traffic processed by the LTM device. However, a packet capture on the server showed differences.
Which change will allow the LTM device to process the traffic correctly?
Community Discussion