QuestionQ53
VerifiedIdentify and Resolve LTM Device Issues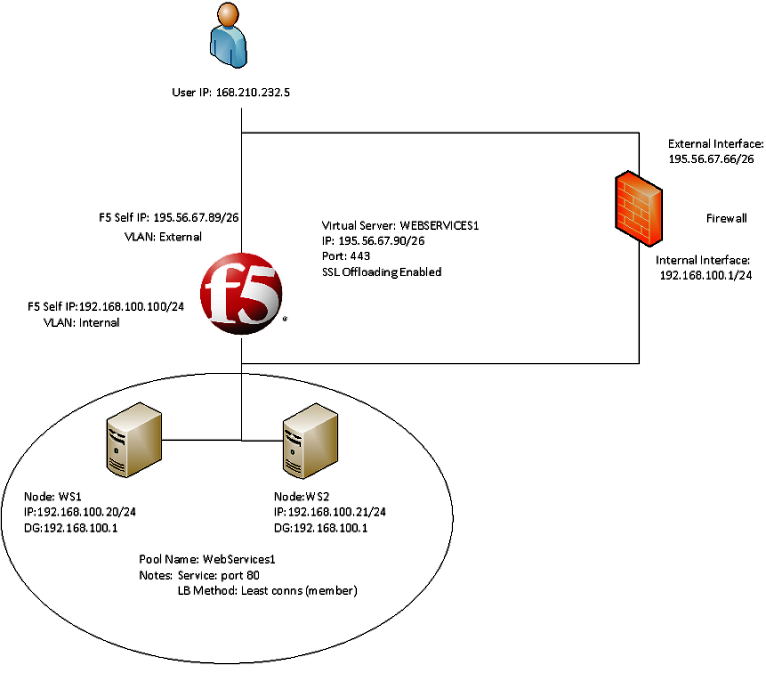
Refer to the exhibit.
Users receive an error when trying to connect to the website https://website.com. The website’s DNS record is 195.56.67.90. The upstream ISP has confirmed that routing between the user and the LTM device has no issues.
The following tcpdump outputs were captured:
External Vlan, filtered on IP 168.210.232.5
00:25:07.598519 IP 168.210.232.5.33159 > 195.56.67.90.https: S 1920647964:1920647964(0) win 8192 <mss 1450,nop,nop,sackOK>
00:25:07.598537 IP 195.56.67.90.https > 168.210.232.5.33159: S 2690691360:2690691360(0) ack 1920647965 win 4350 <mss 1460,sackOK,eol>
00:25:07.598851 IP 168.210.232.5.33160 > 195.56.67.90.https: S 2763858764:2763858764(0) win 8192 <mss 1450,nop,nop,sackOK>
00:25:07.598858 IP 195.56.67.90.https > 168.210.232.5.33160: S 1905576176:1905576176(0) ack 2763858765 win 4350 <mss 1460,sackOK,eol>
Internal Vlan, filtered on IP 168.210.232.5
00:31:46.171124 IP 168.210.232.5.33202 > 192.168.100.20.http: S 2389057240:2389057240(0) win 4380 <mss 1460,nop,wscale 0,sackOK,eol>
What is the issue?
Community Discussion