QuestionQ30

VerifiedIdentify and Resolve LTM Device Issues

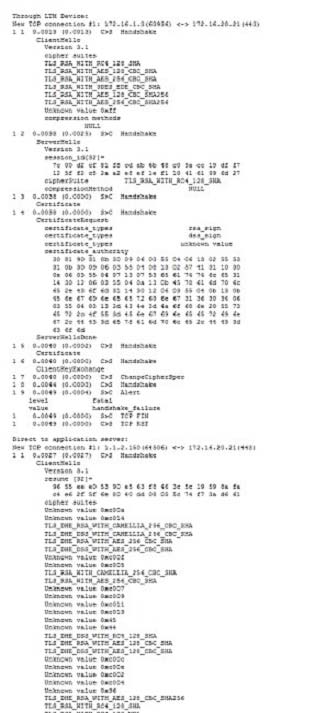
Exhibit

Question Image

Refer to the exhibit.

An LTM Specialist created a virtual server to load-balance traffic to a pool of HTTPS servers. The servers use client certificates to authenticate users. The virtual server has the clientssl, serverssl, and http profiles enabled. Clients cannot connect to the application through the virtual server, but they can connect directly to the application servers.

What is the root cause of this issue?

Explanation

SSL offload terminates the client-to-BIG-IP TLS connection and establishes a separate BIG-IP-to-server TLS connection. The backend server therefore does not receive the client certificate supplied on the original client-side TLS connection, even though it requires that certificate for user authentication. F5 documents that mutual TLS cannot ordinarily pass through a decrypting intermediary because the intermediary does not possess the client private key needed for the new server-side handshake.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!