QuestionQ24
VerifiedRisk Management with Policy Rules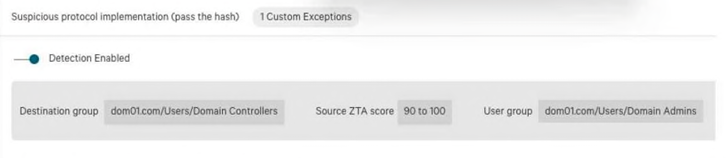
Given the detection exclusion shown, which option correctly explains how it applies to the “Suspicious protocol implementation (pass the hash)” detection?
Given the detection exclusion shown, which option correctly explains how it applies to the “Suspicious protocol implementation (pass the hash)” detection?
Community Discussion