QuestionQ64

VerifiedVulnerability Management

A vulnerability analyst performs a web application scan against an asset that sits behind a load balancer configured for pass-through mode: http://10.203.20.10

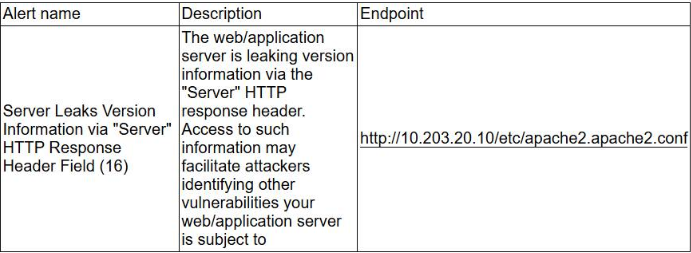
The analyst runs the Zed Attack Proxy (ZAP) tool, performs a scan, and receives the following alert:
Question Image

Which of the following should the analyst recommend as a remediation for this finding while keeping the site operational?

Explanation

The alert identified is ZAP's "Server Leaks Version Information via 'Server' HTTP Response Header Field" finding, which indicates the web/application server is disclosing version details through the HTTP 'Server' response header. This information can help attackers identify known vulnerabilities associated with that specific server version. The official remediation guidance for this alert is to configure the web server, application server, or load balancer to suppress the 'Server' header or replace it with generic, non-version-specific details (for example, using Apache's ServerTokens directive, nginx's server_tokens off setting, or removing the header in IIS). This resolves the disclosure issue without disrupting the site's availability, unlike blocking HTTP traffic outright.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!