QuestionQ51

VerifiedVulnerability Management

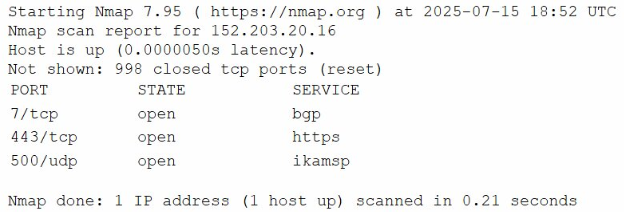
A vulnerability analyst must perform a security assessment on an edge device running various services. The analyst runs an Nmap port scan and observes the following output:
Question Image

Which of the following should the analyst do next to validate that the discovered remote access service is secure?

Explanation

The scan reveals UDP port 500 open with the ikamsp (ISAKMP/IKE) service, which is used to negotiate IPsec VPN tunnels — this is the remote access service in question. IKE Phase 1 can operate in either Main Mode or Aggressive Mode; Aggressive Mode exposes authentication data in cleartext during negotiation and is susceptible to offline PSK-cracking attacks, whereas Main Mode protects this exchange. To validate the security of the VPN service, the analyst should confirm it is configured to use Main Mode rather than the weaker Aggressive Mode.

Community Discussion

No comments yet. Be the first to start the discussion!