QuestionQ47

VerifiedSecurity Operations

A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team. The analyst must:

  1. Identify Linux systems that have successful and unsuccessful logins with username "User1".
  2. Create an output report named "linux-events" of all the events to a flat file.

The analyst issues the following console command:

ls /var/log/

The shortened output of the command is below:
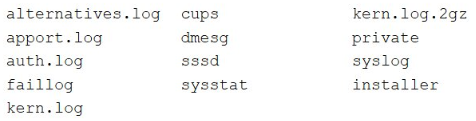
Question Image

Which of the following commands should the analyst use to meet the report output requirements?

Explanation

On Debian/Ubuntu-based Linux distributions, /var/log/auth.log is the log file that records authentication-related events, including both successful and failed login attempts, sudo usage, and PAM authentication activity. Filtering this file with grep for the username "User1" and redirecting the output to a file captures every login event (success and failure) tied to that user, satisfying both requirements of identifying successful and unsuccessful logins and producing a flat-file report. The other listed files do not meet the requirement: sssd refers to a service/directory rather than a consolidated authentication event log, syslog contains general system messages rather than focused authentication data, and faillog only records failed login counts, not successful logins.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!